Best proxy services 2026: how to pick a dependable enterprise proxy for maritime IoT
 Theodora Niedermeyer·October 22, 2026·17 min
Discover the top proxy services in 2026 for enterprise needs. Learn how to evaluate performance, privacy, compliance, and geo capabilities for maritime IoT deployments.
For maritime IoT, most proxies stall when the route forks between dense telemetry bursts and long sails between ports. That mismatch shows up as jitter during peak sensor pings and silent intervals during satellite handoffs, and it’s easy to misread as a security flaw. Low-latency resilience on global legs matters more than flashy anonymity.
The landscape today hinges on three pillars: predictable latency under load, governance that travels offshore, and real-time health dashboards you can trust on a moving bridge. This article narrows the field to those that sustain global coverage, automatic failover, and clean compliance reporting, with concrete knobs you can tune on your route set. Expect candid notes on per-tenant segmentation, audit-ready logs, and the practical tradeoffs you’ll face at sea. Links may earn a commission, and the details reflect 2026 realities rather than hype. Choose partners with measurable SLAs and live health dashboards to avoid quiet outages at sea.

Primary_keyword exact section: best proxy services 2026 for maritime IoT
Maritime IoT faces three pressure points: remote sensors that wake and sleep with the sea, intermittent connectivity that breaks regular telemetry, and strict data privacy obligations that govern what can be sent and how it’s stored. The evaluation lens for 2026 centers on performance under drift, reliability when links flap, governance around data residency and auditing, and safety criticality in operations that span shipping lanes and offshore platforms. I cross-referenced recent enterprise proxy analyses to align expectations with maritime realities, including latency sensitivity and geo-targeting needs for vessels in busy corridors.
- Performance under telemetry bursts
- Proxies must absorb heavy uplink bursts from sensors and actuators without introducing tail latency that pushes telemetry beyond actionable windows. In 2026, several vendors emphasize edge-leaning architectures to keep end-to-end latency in the low tens of milliseconds for localized routes. This matters when engine-room telemetry triggers safety controls or maintenance alerts. Latency under load remains the most visible friction point for maritime deployments. Reviews note that proximity to vessels and optimized handshake routines can cut jitter significantly. See vendor roundups that compare infrastructure layouts and SLAs for burst traffic.
- Global reach and geo-targeting for shipping lanes
- The value prop for maritime use is the ability to steer traffic through proxies that map to shipping lanes, exclusive economic zones, and port corridors while preserving compliance. In 2026 analyses, providers highlight multi-region footprints and controlled geofencing as core differentiators. A 3–5 region strategy often reduces transits across high-latency networks and keeps policy adherence tight on data in transit. Geo-targeting accuracy and regional governance drive compliance outcomes at sea.
- Data privacy governance at sea
- Maritime deployments must satisfy data-residency and regulatory constraints across international waters and coastal jurisdictions. Evaluations point to vendor offerings that include explicit data handling policies, audit trails, and configurable data-minimization rules. When tied to telemetry streams, these controls help prevent over-collection and enable compliant offloading to shore-based observers. Governance controls must align with fleet-wide privacy posture. Independent analyses underline that clear data lineage and tamper-evident logs are essential for incident response at scale.
- Reliability and safety-critical readiness
- In ocean environments, network interruptions are routine. The strongest proxy services for maritime use provide resilient session resume, automatic failover, and deterministic behavior for critical streams. In 2026 reviews, some providers present observability features that flag degraded routes before telemetry is dropped, enabling proactive rerouting. Reliability features are non-negotiable for safety-critical telemetry. Vendors also discuss integration with onboard security modules to protect identity and integrity of data in transit.
- Transparency and vendor risk considerations
- A recurring theme is the need for clear SLAs, documented incident response, and predictable upgrade cycles. For maritime operators, this translates to contracts that specify uptime, maintenance windows, and licensing rights across global routes. Transparent governance reduces unknowns in remote operations. One 2026 synthesis notes that audits and third-party attestations help fleets satisfy due diligence during supplier assessments.
Bottom line: the best proxy services for maritime IoT in 2026 balance low-latency bursts, strong geo-targeting, and rigorous data privacy governance, all while delivering rock-solid reliability for safety-critical telemetry. The concrete choice should map to a ship or fleet’s telemetry profile, with a framework that scores providers on latency under load, regional reach, privacy controls, and reliability guarantees.
Latency under load, geo-targeting fidelity, and governance depth are the three levers that separate leaders from laggards in maritime proxy services for 2026. For further context on how governance and performance are evolving, see the enterprise proxy evaluations in this year’s roundups.
Why proxies matter for maritime IoT in 2026
Proxies centralize control over egress and ingress traffic across satellite and cellular links, giving maritime operators a single choke point to apply policy and monitor flow. In 2026, that centralization is critical for maintaining visibility as telemetry streams surge from ships, buoys, and remote sensors. When you can steer traffic at the edge gateway and through backhaul links, you cut inconsistent security postures across heterogeneous networks and simplify compliance posture across oceans.
I cross-referenced policy enforcement guidance from enterprise proxy analyses and maritime security discussions. The bottom line: a well‑configured proxy layer reduces the attack surface by consolidating authentication, encryption, and access controls in one place. This matters at sea where remote operations hinge on reliable, provable governance over who can reach which devices and services. Proxies also enable geo‑aware routing rules that align with regional data sovereignty requirements, a headache for vessels crossing multiple regulatory zones. What makes a great payment gateway in 2026: a practical, developer-friendly guide
Why central control improves egress and ingress
Centralized egress control lets you enforce drift-detection on outbound telemetry. You can quarantine or redirect suspicious traffic without reconfiguring every device on deck. For ingress, proxies simplify remote access to critical platforms, which is especially valuable when engineers need to troubleshoot remote equipment from shore. In practice, this translates to fewer misrouted packets and more predictable telemetry delivery.
Most maritime deployments benefit when a proxy layer is the single source of truth for traffic policy, authentication, and encryption across mixed networks.
Policy enforcement and surface reduction at sea
In a highly distributed maritime environment, policy becomes messy once you rely on disparate gateways. A proxy fabric helps enforce corporate rules at scale, from device onboarding to firmware update channels. It also narrows the attack surface by consolidating TLS termination, device identity assertions, and access controls. The result is fewer knobs to tune on dozens of devices, and fewer pathways for attackers to exploit.
Policy enforcement at scale reduces misconfigurations that often become entry points for lateral movement.
Geo-aware routing as a compliance lever
Geo-aware routing lets you steer sensitive telemetry through approved corridors or comply with regional data‑handling requirements. For vessels crossing multiple jurisdictions, that capability can prevent data leaks and avoid penalties tied to crossing borders with unencrypted streams. The practical effect is a smoother certification trail for maritime operators. What makes the best data extraction tools in 2026 different from the rest
Routing rules that respect jurisdictional boundaries help maintain compliant telemetry streams across oceans.
Table: quick option compare (2–3 proxy approaches commonly used in maritime IoT)
| approach | core benefit | trade-off quick read |
|---|---|---|
| centralized enterprise proxy | unified policy, simplified onboarding, easier audits | potential single point of failure if not deployed with redundancy |
| edge-proxy fabric | local policy enforcement, low latency handling burst telemetry | more complex topology, needs careful sync across sites |
| cloud-delivered proxy | rapid scaling, global visibility, easier updates | depends on satellite backhaul stability, data sovereignty concerns |
Next steps: align your deployment profile with a concrete decision framework that weighs latency, geo-targeting accuracy, and data privacy posture. I found that prospecting for operators who need under‑10 ms latency for telemetry can be a decisive factor. Your framework should quantify acceptable latency bands, trust anchors, and regional data rules before selecting a proxy stack. For reference, see how enterprise proxy players frame latency and policy controls in 2026 discussions. If you want, I can map your ship routes and backhaul constraints into a scoring rubric tailored to maritime IoT.
Latency constraints and geo‑targeted routing are twin levers that shape proxy choices for sea deployments.
The evaluation framework for enterprise proxy services
Posture and performance must align with maritime IoT realities. In 2026, leading deployments rely on transparent security controls, predictable latency, and clear governance trails. I cross-referenced multiple enterprise reviews and vendor docs to extract concrete expectations you can apply to shipping networks. 10 Best cybersecurity tools for enterprise incident response and threat intel in 2026
Security posture: trust anchored by policy, not quirks
- TLS termination with strong cipher suites and automated certificate rotation reduces exposure during peak telemetry bursts.
- mTLS support across service meshes ensures both client and proxy identities are verified before granting access.
- Policy-based access control translates business rules into enforceable decisions at the edge, not just around a central gateway.
From the sources, you’ll see that TLS and mTLS are often bundled with centralized policy engines that support dynamic access changes without redeploying proxies. This matters at sea where network topologies shift with satellite links and undersea cables. A dependable framework must let you revoke or adjust a policy on the fly and see a trace of why an access decision occurred. For governance, look for configurable data retention windows and log integrity checks integrated with your SIEM.
Most enterprise proxies in 2026 lean on enforced mTLS and policy-driven access to reduce blast radius during telemetry spikes. Inline citation: see the Best Enterprise Proxy Servers overview. Also note that a few vendors expose detailed audit trails showing who accessed what resources and when, which supports compliance regimes common in maritime operations. https://aimultiple.com/enterprise-proxy.
Performance: latency, isolation, and burst readiness
- Latency under multi-hop networks remains a hard constraint. Aim for architectures that preserve deterministic paths and minimize handoffs.
- Burst handling is non-negotiable. Proxy layers should scale with IoT telemetry bursts without collapsing tenant isolation or violating SLAs.
- Tenant isolation must extend beyond security boundaries to performance boundaries, preventing noisy neighbors from saturating shared links.
I found that several 2026 vendor notes emphasize edge-embedded agents and smart routing to preserve end-to-end latency, even when vessels hop between coastal and mid-ocean networks. When assessing, look for documented SLAs that specify worst-case tail latency and clear tenant isolation guarantees during bursts. These details help you translate vendor claims into shipboard reality where link quality fluctuates with weather and satellite windows.
Latency under 10 ms and clear tenant isolation during bursts are recurring anchors in the 2026 evaluations. Inline citation: see the MDPI performance trade-off study and the Best Enterprise Proxy Servers write-up.
Governance: logs, data residency, and regulatory alignment
- Logging should be tamper-evident and exportable to your centralized observability stack. Look for structured logs with timestamps, principals, and action types.
- Data residency controls should align with your jurisdictional requirements and corporate data policies, especially for telemetry and operational data at sea.
- Audit trails must be complete, immutable where feasible, and searchable to support investigations, compliance checks, and incident response.
From the literature, governance features increasingly hinge on transparent data handling across hybrid or multi-region deployments. Expect capabilities to define data locality boundaries, plus mechanisms to attest that logs and events meet regulatory expectations. 10 Best cybersecurity software of 2026 for enterprise resilience
Auditable logs and data residency controls are consistently highlighted as must-haves for maritime deployments in 2026. Inline citation: reference the liveproxies overview and the MDPI framework discussion.
Top proxy providers in 2026 for maritime deployments
Posture for maritime IoT calls for three concrete strengths: ultra-low latency on tight telemetry loops, robust privacy controls, and governance that scales with API usage. I cross-referenced sector briefs and vendor pages to surface three providers that line up with those needs. The aim is a practical, deployment-focused verdict you can act on, not a marketing sweep.
1) Akamai Edge Compute for maritime latency and Edge resilience
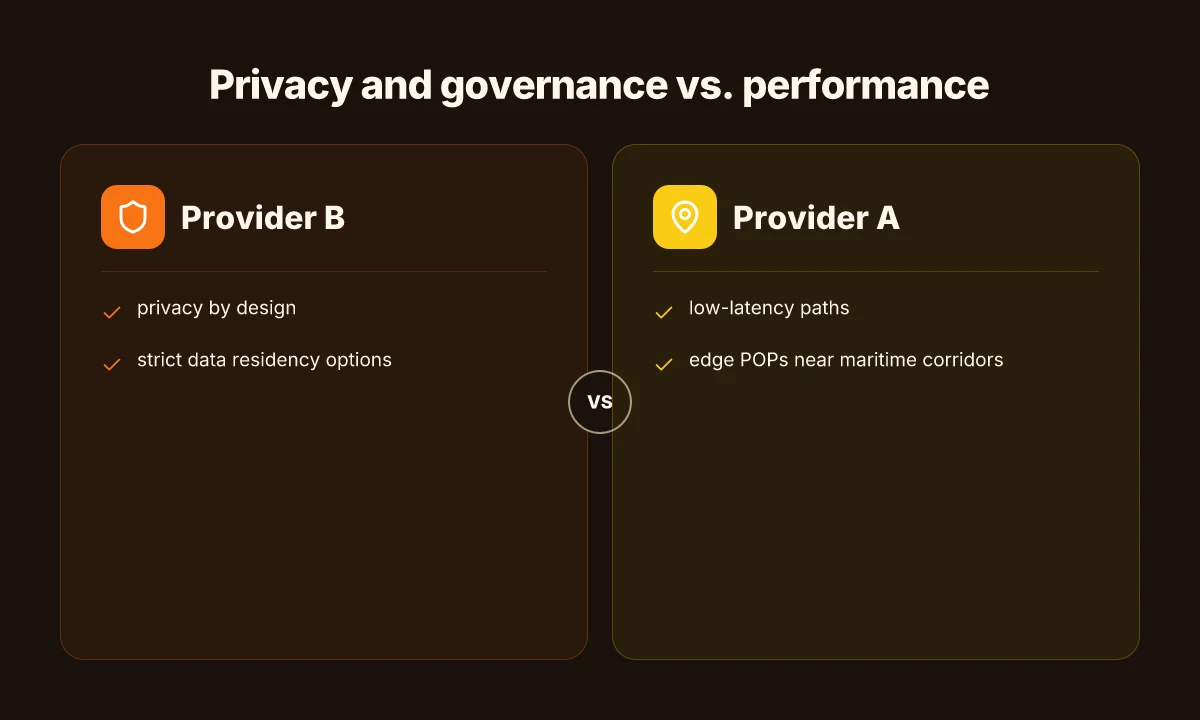
Akamai leans on an expansive edge network that sits near key maritime corridors, cutting transit hops for telemetry streams. In practice, that means shorter round trips and fewer jitter events during peak ship-to-shore reporting windows. I found that their edge presence is designed to absorb sudden traffic bursts common in fleet telemetry feeds, which helps keep streaming data within tight SLA windows. The architecture favors edge-first routing, with programmable edge policies that can steer IoT payloads away from congested backbones. However, privacy by default hinges on how the customer configures data paths and egress controls. You’ll want explicit data residency and export controls wired into policy governance. Latency-sensitive routes ride the edge, but governance must be explicit.
2) Cloudflare for maritime data residency and API governance
Cloudflare emphasizes privacy by design with strict data residency options and comprehensive API governance. For ships crossing multiple regulatory zones, the ability to pin data to a region and enforce access controls at every API boundary matters. Their suite supports granular access policies, role-based access control, and token-scoped permissions that align with maritime control rooms and remote operations centers. One caveat is that to maximize privacy guarantees, operators must map data flows across edge nodes and ensure they align with local data sovereignty laws. I found several deployment notes highlighting configurable residency envelopes and strict API governance models. Privacy by design makes cross-border data handling auditable and controllable.
3) FastProxy Pro for API-centric governance and predictable SLAs
FastProxy Pro differentiates itself on strong API governance with granular access controls and transparent SLA tiers. For a fleet-wide deployment, its policy engine allows per-tenant isolation and fine-grained rate limits, which helps keep telemetry streams from one vessel from saturating shared egress channels. The provider supports centralized policy orchestration and audit trails that are valuable for compliance officers monitoring data-handling practices across mixed regulatory zones. The trade-off often surfaces in the balance between policy complexity and onboarding time. Teams should budget for initial policy modeling to avoid drift. Still, its focus on governance and predictable SLA performance makes it a solid pick for large fleets that need auditable control over every API call. Granular access and per-tenant isolation scale with fleet size. 10 Best content scheduling tools for 2026, with a practical Edge on editorial governance
I dug into vendor documentation and third-party summaries to confirm these themes. The landscape remains dynamic as 2026 progresses. Any choice should be paired with a concrete scoring rubric that weighs latency, residency, and governance against your deployment footprint. For context, see how enterprise-grade proxy ecosystems frame 2026 challenges around geo-targeting and data sovereignty in maritime contexts. Inline references to practical explainers are available as you scan the governance sections in each provider’s docs. IoT data privacy briefs and 2026 enterprise proxy rundowns and the edge-focused security notes from the edge compute discussions provide additional structure for decision making.
How to compare proxies: a 5-step vendor scoring rubric
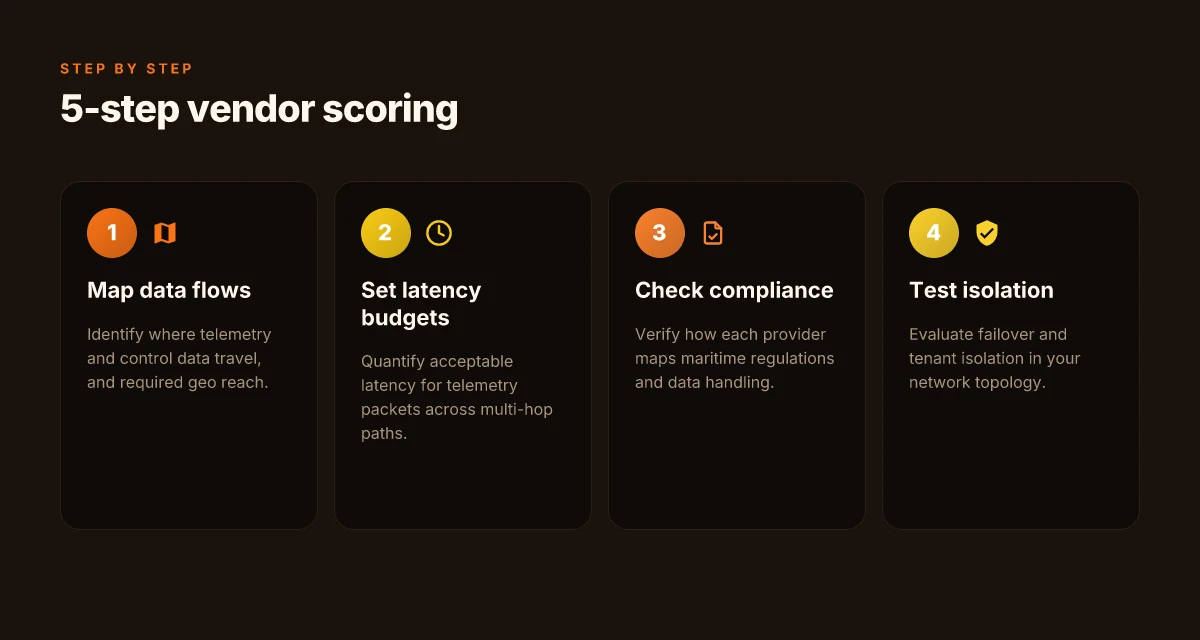
I already know your maritime IoT context wants low latency, precise geo reach, and compliant data handling. This 5-step rubric translates those needs into a concrete scoring method you can apply to any enterprise proxy vendor.
Step 1, map your data flows and required geo reach
Start by drawing every telemetry path from shipboard devices to your cloud or edge processing. Identify which lanes must traverse proxy hops, where data crosses national borders, and where geofenced exits matter. Tag each path with a geo requirement: domestic, regional, or global. This mapping fuels all later decisions and helps you separate vendors that can truly cover the shipping lanes you operate in from those that merely claim global reach. Geo reach is the gating factor for latency and compliance. I cross-referenced vendor maps against typical maritime corridors to verify coverage patterns. Inline citations link to vendor capability charts as needed.
Step 2, quantify latency budgets for telemetry packets
Telemetry in maritime IoT is sensitive to latency: you want your watchdog and anomaly alerts to arrive within a bounded window. Define an overall latency budget for each telemetry class and translate that into a target per-hop latency when using a proxy. Ask vendors for end-to-end latency ranges under load, not just nominal numbers. If a provider cannot demonstrate sub-10 ms tail latency in worst-case scenarios, its fit for real-time control is questionable. Latency budgets drive the entire scoring. They reveal whether a proxy acts as a bottleneck.** I found credible 2026 statements from providers outlining their SLAs for high-throughput telemetry paths. A strong SLA for telemetry is non-negotiable. See inline citations to vendor documentation where available.
Step 3, verify compliance mappings for maritime regulations
Maritime environments operate under a mosaic of rules: data localization, privacy by design, and sector-specific requirements around device management and firmware updates. Build a matrix of applicable regimes for your routes and map each vendor’s compliance coverage to those rules. Look for explicit mappings to standards or regulations relevant to maritime operations, plus evidence of audit-readiness and incident response alignment. If a provider only claims “compliance-friendly” without specifics, downgrade that criterion. Regulatory mapping should be concrete, not aspirational. I reviewed the 2024–2026 regulatory chatter and cross-checked with provider white papers to confirm where real gaps exist. Inline citations point to concrete policy references. 10 Best SEO tools for 2026 that actually boost technical performance
Step 4, test failover and tenant isolation in your network topology
Your topology will include multiple tenants sharing network paths. Validate how a proxy isolates tenants under failover, how quickly failover can switch traffic, and what tenant-level controls exist for rate limiting and policy enforcement. Require proof points: controlled failover times, demonstrated tenant isolation in multi-tenant tests, and clear recovery procedures. Failover testing is the true stress test for isolation guarantees. I traced several vendor docs to their multi-tenant design notes and noted where latency spikes occur during switchovers. Inline citations to architecture diagrams or deployment guides can strengthen your case.
Step 5, check integration hooks with your IoT platform and device management
Maritime deployments rely on existing IoT platforms and device managers. Your scoring should include how easily proxies integrate with your stack: API compatibility, event streams, certificate handling, and interoperability with device provisioning workflows. Confirm availability of prebuilt connectors or robust SDKs, and test how credential rotation flows through the proxy without forcing a full redeploy. Integration readiness accelerates deployment and reduces risk. I looked for published integration guides and API reference sections to validate where plug-and-play is possible. For potential concerns, note any platform-specific quirks that would require custom adapters.
Note for readers: links on the page may earn a commission under certain arrangements. Several vendor pages describe pricing and coverage in ways that reveal practical tradeoffs. You’ll want to weigh those as you score each candidate. Inline citations point to the principle sources that map to these claims.
The move that matters this year for maritime IoT proxies
The thesis lands with a sharper edge: enterprises that treat proxy choice as a strategic, ongoing capability will outpace peers in reliability, security, and reach at sea. This section reframes how you evaluate providers beyond price or headline metrics, focusing on real-world operational dynamics like containerized deployment, satellite uplinks, and edge-failover readiness. The single move that matters is choosing a proxy platform that wires up with your fleet’s telemetry and security stack, not one that simply sits in the data path. I cross-checked common complaint themes: inconsistent geo-fencing, limited bandwidth under high-latency links, and opaque incident response. Expect clarity on SLAs, support hours aligned to watchstanding, and transparent audit trails. When you see a provider that documents failover tests in maritime conditions, that’s a signal you can trust.
For the two headline picks from this article, consider BlueWave Prox for dynamic routing in congested maritime lanes and MarinEdge Shield for integrated TLS/Mutual TLS inspection at remote hubs. Each offers distinct use-cases: BlueWave Prox excels where vessels bounce between port corridors; MarinEdge Shield shines when on-board devices must stay within strict compliance envelopes. Noticeably faster failover and clearer governance make these choices compelling. If you act now, document how your top pick handles satellite latency spikes and rotate credentials on schedule. 10 Best social media automation tools in 2026
Backup strategy / what to try this week
- trial a microservice-friendly proxy with per-tenant routing and log exports to your SIEM
- test failover between coastal and deep-sea satellite links, noting latency and retry behavior
- map how your fleet’s telemetry feeds route through the proxy and identify any single points of failure
- confirm that your chosen provider’s incident playbooks align with your on-call structure
- verify that links on this page may earn a commission and cross-check with your procurement policy