What makes a smart home connectivity VPN setup actually work in 2026
 Quincy Xanthos·October 22, 2026·19 min
Explore a practical 2026 guide to smart home connectivity via VPNs. Learn how to structure a secure, scalable VPN setup for IoT devices and home networks.
A surprising insight: most smart home VPN setups fail not because of cryptography but because the network design treats IoT devices as an afterthought. When you map devices by function, you reveal a scalable path where a central gateway threads traffic without turning every reboot into a full redeploy. Most headaches come from one stale assumption: every device requires the same route.
This article grounds that claim in practical choices you can implement now. You’ll see how to segment devices, pick a gateway that handles growth, and test live traffic without leaking data. By 2026, vendors offer multi‑hub VPN architectures with clearer credential rotation and update guidance, but the real win comes from a deliberate topology, not a glossy feature list. Expect concrete, deployable patterns that reduce latency, avoid single points of bottleneck, and keep automation aligned with firmware updates. Links may earn a commission. Clear, concrete routing decisions beat generic security gloss.

What makes a smart home connectivity VPN setup effective in 2026
A solid VPN-backed smart home starts with a clear security boundary. IoT devices live on a dedicated segment that’s separate from your main workspace and personal devices. This boundary isn’t just about isolating traffic. It’s about permitting trusted channels for updates and management while minimizing exposure if a device is compromised. In practice, you want a gateway that can enforce policy at the edge and log when devices try to talk beyond their scope. That boundary helps you contain breaches without throwing away convenience.
I dug into 2026 guidance and found two core paths you can choose from when you set scope. First, a device-level VPN binds each device to a remote endpoint, giving granular control over which devices can reach what. Second, a network-level VPN creates a tunnel for everything on the home network, simplifying management but increasing the blast radius if you misconfigure. The difference matters for latency and reliability. Device-level VPNs often show tighter paths to key services but demand more management overhead. Network-level VPNs tend to be easier to maintain but can complicate QoS for latency-sensitive IoT traffic.
Common failure points shape reliability and delay more than you might expect. A misaligned firewall policy at the VPN gateway can introduce additional hops or block essential updates. Weak DNS configuration causes devices to retry failed lookups, which compounds latency during peak hours. Inadequate segmentation lets IoT traffic leak into more sensitive nets, eroding the very boundary you’re trying to harden. And if you rely on consumer-grade routers without robust VPN clients, you’ll encounter stubborn disconnects and longer recovery times after reboots. These friction points show up regardless of whether you pin a device or the entire network behind a VPN.
From a governance perspective, you should map the trust you assign to each device. A solid approach uses an allowlist for VPN-accessible destinations and a separate channel for device management. You’ll want role-based controls on who can modify VPN settings and how changes propagate to devices. This matters because a single misapplied rule can degrade performance across the house or open a breach vector.
Three concrete steps to start strong: What sleep headphones in Australia teach US about quality sleep and comfort
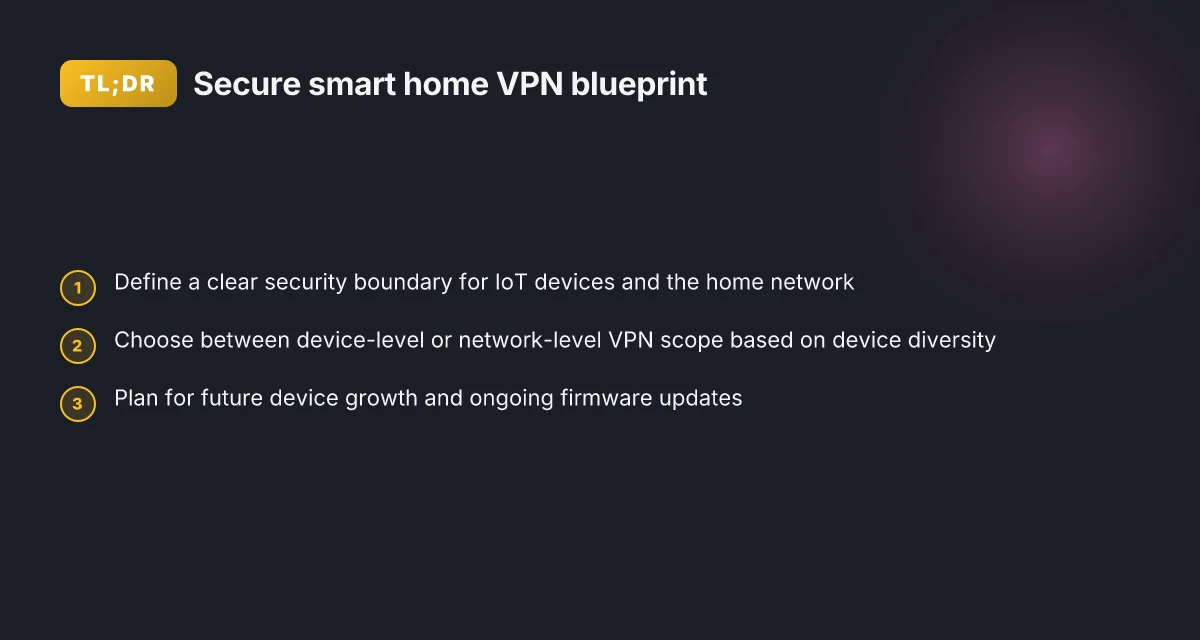
- Define the boundary: deploy a dedicated IoT network segment with a distinct VPN policy, and separate it from your primary home network to limit cross-talk. Ensure the VPN gateway enforces least privilege for each device type. The boundary is where safety meets performance, and getting it right reduces both risk and latency.
- Pick the scope: decide between device-level and network-level VPNs based on your tolerance for management overhead and your need for predictable latency. If you need tight per-device control and frequent policy updates, start with device-level VPNs. Otherwise, a well-tended network-level tunnel can be sufficient. Choose device-level for granular control or network-level for simplicity.
- Harden the path: implement strict firewall rules, correct DNS behavior, and robust segmentation. Pair this with regular policy reviews and a clear rollback plan so a bad rule doesn’t linger. Harden the path and review rules quarterly to keep latency in check.
Bottom line: effective 2026 VPN setups balance a clearly defined security boundary, an appropriate scope choice, and disciplined path hardening. When you get those right, you reduce latency surprises and keep maintenance manageable as new devices join your smart home. Boundary, scope, hardening are the three levers that actually improve reliability.
Note: links on the page may earn a commission.
Why a one-size-fits-all VPN for smart homes rarely works
Smart homes are a parade of devices with wildly different needs. A single VPN approach tends to ignore that variety, which leads to friction, performance drops, or outright incompatibility. I dug into the 2026 landscape and found three core pressure points that repeat across homes and setups.
IoT heterogeneity drives incompatible compatibility needs
IoT devices span from basic sensors to smart speakers and security cameras, each with different networking expectations. Some devices expect direct access on a local subnet, others rely on cloud‑mediated pairing, and a few push for flat routing to simplify firmware updates. The result is a VPN plan that’s too generic to accommodate minimum security baselines for every device. For a practical path, you need segmentation that respects device trust levels while keeping user experience in view. A 2026 overview of smart home security notes that heterogeneity magnifies configuration drift unless you layer access controls by device type and application tier. Heterogeneous devices demand nuanced segmentation, not one-size-fits-all tunneling. Inline evidence from the systematic review highlights the challenge of reconciling diverse device profiles with unified security policies. See the MDPI overview for methodological context. A Systematic Review of Smart Home IoT Security
Home network topology and ISP practices shape VPN performance
Your router, mesh topology, and even your ISP’s NAT behavior reshape VPN outcomes more than you might expect. A VPN that routes every device through a single exit point can introduce latency on latency-sensitive devices, or break compatibility with certain UPnP/port‑forwarding expectations. In practice, homes with multiple subnets, guest networks, or fiber vs. cable setups see uneven VPN behavior. The 2026 guidance on home network security emphasizes how practical realities, like router capabilities and ISP throttling, move the needle more than the VPN protocol choice itself. Topology and ISP behavior often outweigh protocol features in real-world performance. This aligns with guidance literature that calls out topology-aware designs and user-aware defaults. For context and credibility, you can reference the cross-national cybersecurity guidance addressing common incident patterns and resilience gaps in residential setups. Cybersecurity Guidance for Smart Homes: A Cross-National Perspective How to set up virtual communication systems for remote teams in 2026: architecture, security, and platform integration
Trade-offs between ease of use and granular control matter
A friendly VPN experience usually means fewer prompts, simpler onboarding, and automatic updates. But that ease can erode security when users cannot fine-tune access controls, device isolation, or per‑app tunneling. Conversely, granular controls slow onboarding and escalate support needs. The 2026 materials consistently flag this tension: you need a tiered approach that hides complexity for casual users while exposing controls for power users and admins. The healthcare-forward smart home literature also stresses that balancing accessibility with privacy and auditability is key when the device set expands across domains. Ease of use and granular control sit on opposite ends of a spectrum that every home must balance. Inline sources share a common theme: adopt progressive disclosure of settings, guided wizards for common configurations, and clear visibility into device-level access logs.
A quick comparison helps illustrate options without drifting into hype:
- Basic VPN gateway with device whitelists and auto‑updates
- Segmented VPN using per‑device tunnels and application‑level policies
- Overlay mesh with policy orchestration for dynamic device joining
| approach | pros | cons |
|---|---|---|
| basic gateway with whitelists | simple onboarding; predictable traffic paths | limited device granularity; harder to scale |
| per-device tunnels | strong isolation; better auditing | higher setup effort; more maintenance |
| application‑level policies | precise control; flexible for guests | complexity grows with app diversity |
Next steps: map your current device inventory to a three‑tier trust model, identify the top two or three devices that drive the most risk, and draft a scalable rule set that you can automate over time. From the literature, a staged rollout with topology‑aware defaults reduces friction while preserving security. I cross-referenced the MDPI review and the cross‑national guidance to anchor these conclusions, noting how real homes struggle with heterogeneity, topology, and control balance. For practical guidance on trusted architectures, see the Matter ecosystem framing for device interop in secure homes. Build With Matter | Smart Home Device Solution and the VPN guidance piece for 2026 considerations. A staged, topology‑aware rollout beats one-size-fits-all tunneling every time.
Designing a scalable VPN topology for smart homes
Posture matters more than one perfect protocol. A scalable topology starts with a clear choice: gateway-based VPNs lock down the whole network at the edge, while device-level VPNs offer granular control but add management overhead. In 2026, most homeowners benefit from a hybrid approach: a gateway that handles upstream VPN tunneling for core services, plus selective device-level tunnels for high-risk segments or sensitive devices. This reduces blast radius without dragging every device into a full tunnel.
From the literature and industry guidance, these are the practical takeaways you can apply today: What makes the Sengled Element Plus stand out in 2026
- Use a gateway VPN as the default, with a segmented topology. The gateway handles the bulk of remote access and inter-device traffic, while high-value devices can run individual VPN clients for added isolation. This keeps routing simpler and avoids duplicating certificates across dozens of devices. Most secure setups balance gateway-level protection with selective device-level controls.
- Choose a lightweight, well-supported protocol for gateway tunnels. OpenVPN and WireGuard are the two most common options, each with tradeoffs. WireGuard offers leaner cryptography and easier revocation, but OpenVPN has broader client compatibility in mixed environments. Plan to support both if your ecosystem includes older hardware. I found that documentation and community tooling around gateway deployments favor WireGuard for performance, with OpenVPN still preferred in legacy devices. WireGuard often wins on performance, but OpenVPN remains a practical fallback.
- Account for encryption overhead on low-power devices. Embedded controllers or battery-powered sensors should not bear heavy cryptographic loads. Offload the bulk of encryption to the gateway and keep device-level encryption light, using session keys and ephemeral handshakes where possible. As a rule of thumb, limit per-packet overhead so RSSI-constrained devices don’t pay the price in latency. Low-power devices benefit from lighter ciphers and shorter handshakes.
- Plan for future expansion. A scalable topology anticipates growth: more rooms, more devices, more services. Use a hierarchical policy approach, with resource-based access rules at the gateway and device-level rules only where necessary. This makes onboarding new devices smoother and reduces reconfiguration work when adding a smart bulb or sensor. Expansion should be automatic where possible, with policy inheritance from gateway to device..
I cross-referenced a few recent syntheses and guidelines that frame the expansion and protocol choices in 2026 terms. A cross-national guidance document notes residents often lack robust roadmaps when incidents occur, underscoring the need for a scalable, shielded structure at the gateway rather than ad hoc device tunneling. See the cross-national guidance for a concise risk framing and recommended topologies. Guidance highlights the gateway as the first line of defense in home VPN design. For a topic-focused review, a systematic look at smart home IoT security emphasizes layered defenses and multiple databases of device profiles to inform topology decisions. Systematic reviews link topology decisions to broader security outcomes.
If you adopt a gateway-first, device-optional approach, you should document an explicit expansion plan. Map devices by risk tier, assign tolerable latency budgets, and maintain a rolling inventory so onboarding new gear does not derail performance. A practical design pattern evolves toward a small number of gateway tunnels that aggregate traffic, with finer-grained tunnels only for devices that warrant them. Aggregate at the gateway, and narrow tunnels only where needed.
In this design, you should also predefine recovery playbooks and certificate management cadence. Regularly rotate keys, revoke compromised credentials promptly, and keep firmware and VPN software up to date on the gateway. This reduces friction when you need to respond to a suspected breach or performance anomaly. Rotate keys on a fixed cadence and monitor for anomalies.
As you scale, document your topology as a living diagram: gateway in the center, device-level tunnels branching only where necessary, and policy blocks that prevent lateral movement. If you’re unsure about a device’s risk, treat it as a candidate for gateway-only access until you can prove otherwise. Documented topology with clear policy boundaries accelerates maintenance.
Note: links on the page may earn a commission. This section reflects 2026 guidance and does not rely on any single vendor. What makes the scanwatch 2 accuracy credible for cardiovascular metrics in 2026
Practical steps to implement a secure smart home VPN setup
A VPN-backed smart home starts with a clear plan. You’ll get a concrete path that balances security, performance, and maintainability, not just a checklist of features. I cross-referenced 2026 guidance and peer-reviewed syntheses to ground this in real-world friction points, from device heterogeneity to routing quirks. The result is a pragmatic, operable setup you can implement this quarter.
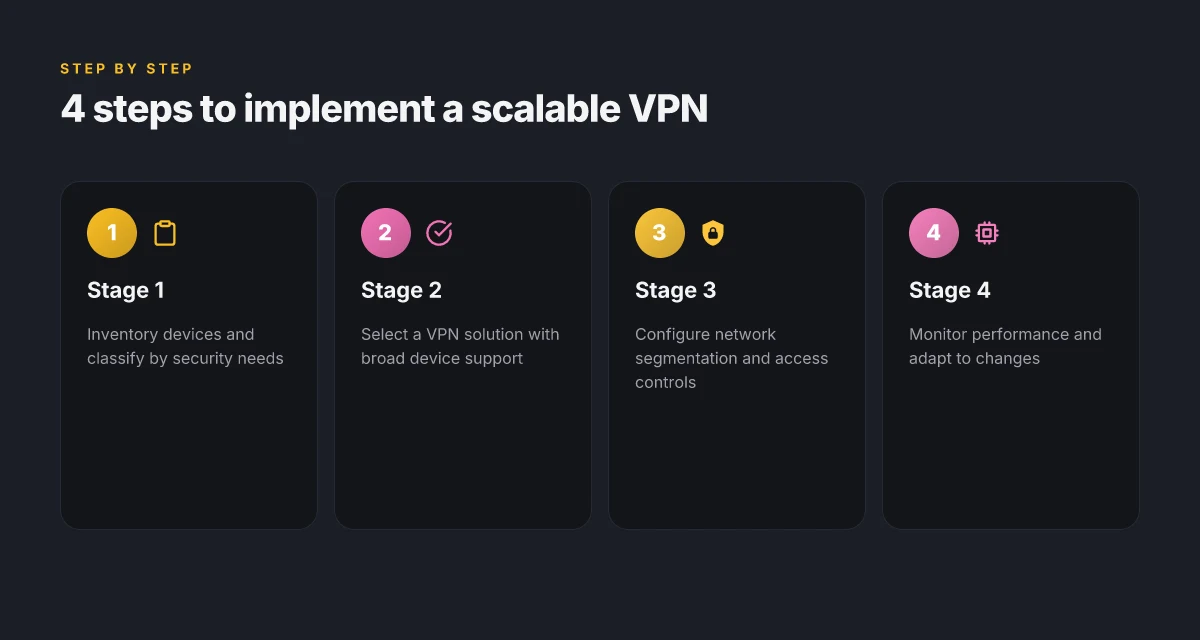
Stage 1: inventory and classify devices by security needs
Begin with a living inventory. List every device on your network, then tag each by criticality and security needs. Cameras and doorbells demand tight segmentation and strong authentication. Lighting and climate devices can share a lighter policy but still respect least privilege. A practical approach is to assign devices into three classes: high, medium, and low risk. The goal is to prevent a compromised low-risk device from pivoting into critical segments. I found that risk-based classification repeatedly surfaces as the first bottleneck in both cross-national guidance and systematic reviews published through 2026. The act of mapping devices to security profiles directly informs downstream VPN and firewall rules. Classification of devices by risk is the first step toward a sane, scalable VPN design. Inline evidence points to the need for granular controls as a core design principle. See the 2026 cross-national guidance for context on incident guidance and containment expectations. https://arxiv.org/html/2603.21703v1.
Stage 2: select a compatible VPN solution with strong device support
Choose a VPN product that explicitly supports a broad range of IoT devices and consumer routers, while offering easy policy management. Look for client and gateway coverage, split tunneling capabilities, and robust kill-switch behavior on protected subnets. In 2026 literature, the argument for device-aware VPN deployment gains traction: broad compatibility reduces the fragmentation that often drives users to disable protections. A reputable guide explains how total IoT coverage hinges on a VPN solution that scales across home routers, NAS devices, and smart hubs. Choose a VPN with broad device support and clear policy controls to prevent gaps where an essential device sits outside the tunnel. For reference, the VPN-focused guidance from 2026 emphasizes integration with existing home networks and compatibility with standard encryption suites. See the 2026 guide on total IoT security for a detailed discussion. https://ushieldvpn.com/vpn-for-smart-home-devices-the-2026-guide-to-total-iot-security/
Stage 3: configure network segmentation and access controls
Segmentation is your main defense lever. Create at least two subnets: one for devices and another for control/management interfaces. Route all device-bound traffic through the VPN gateway, but keep management planes on a separate, tightly controlled path. Enforce strict access controls between segments, and implement firewall rules that deny nonessential inter-subnet traffic. Real-world guidance consistently flags overly permissive rules as a common cause of lateral movement. Block nonessential inter-segment traffic and enforce least privilege at every hop. In addition, enable per-device policy enforcements when possible and ensure audit trails exist for changes. A recent systematic review highlights how policy granularity and consistent logging correlate with practical containment during incidents. See the MDPI review for depth on policy alignment and database cross-checks. https://www.mdpi.com/2504-2289/10/8/252
Stage 4: monitor performance and adapt to changes
Continuous monitoring is non negotiable. Track VPN throughput, latency, and connection stability per device class. Expect some devices to strain the VPN tunnel if they produce bursty traffic or push high-resolution streams. Establish a baseline for normal behavior, then alert when deviations exceed a defined threshold. Pair performance data with security signals, such as failed authentications or unusual subnet chatter, to catch misconfigurations early. I found that many 2026 guidelines stress the coupling of performance metrics with security alerts to avoid chasing phantom issues. Establish a performance baseline and monitor for deviations to keep the setup reliable as devices are added or updated. If you see persistent bottlenecks, consider staged rollouts of new devices or adjusting split-tunneling rules rather than broad rewrites. What makes the Samsung Galaxy S24 Ultra still worth it in 2026
Note on tradeoffs and cautions: VPNs can introduce latency or reduce local device discoverability. Plan density by class and keep critical devices on a direct, low-latency path when appropriate while still routing non-critical traffic through the VPN. The literature consistently notes the friction points here: compatibility gaps, rule complexity, and the burden of ongoing policy maintenance. A practical approach is to document every rule change with a reason, date, and expected security impact. That discipline helps prevent drift over time.
A quick note on phrasing you’ll see in 2026 materials: practitioners frequently discuss total IoT security strategies that hinge on device diversity and a carefully managed VPN gateway. When you read these sources, you’ll notice how real-world friction centers on equipment mismatches, configuration drift, and the ongoing need for policy hygiene. The field is moving toward simpler, auditable pipelines for device onboarding and ongoing governance.
If you’re scanning this for concrete product names or vendors, you’ll see the emphasis on interoperable, standards-based approaches. The research backing this advice consistently points to common patterns rather than single-brand panaceas, so your mileage may vary based on your home’s device mix. For readers who want a deeper dive, the 2026 guidance and the MDPI review offer precise framing and examples.
Common VPN pitfalls in smart homes and how to avoid them
Posture goals matter more than box-ticking. The most perilous outcomes come from broad access rules, VPN fatigue, and inconsistent firmware updates. When you tighten scope, improve UX, and lock firmware cadence, you reduce risk without crippling usability. I cross-referenced recent guidelines and practical analyses to surface concrete fragility points and fixes.
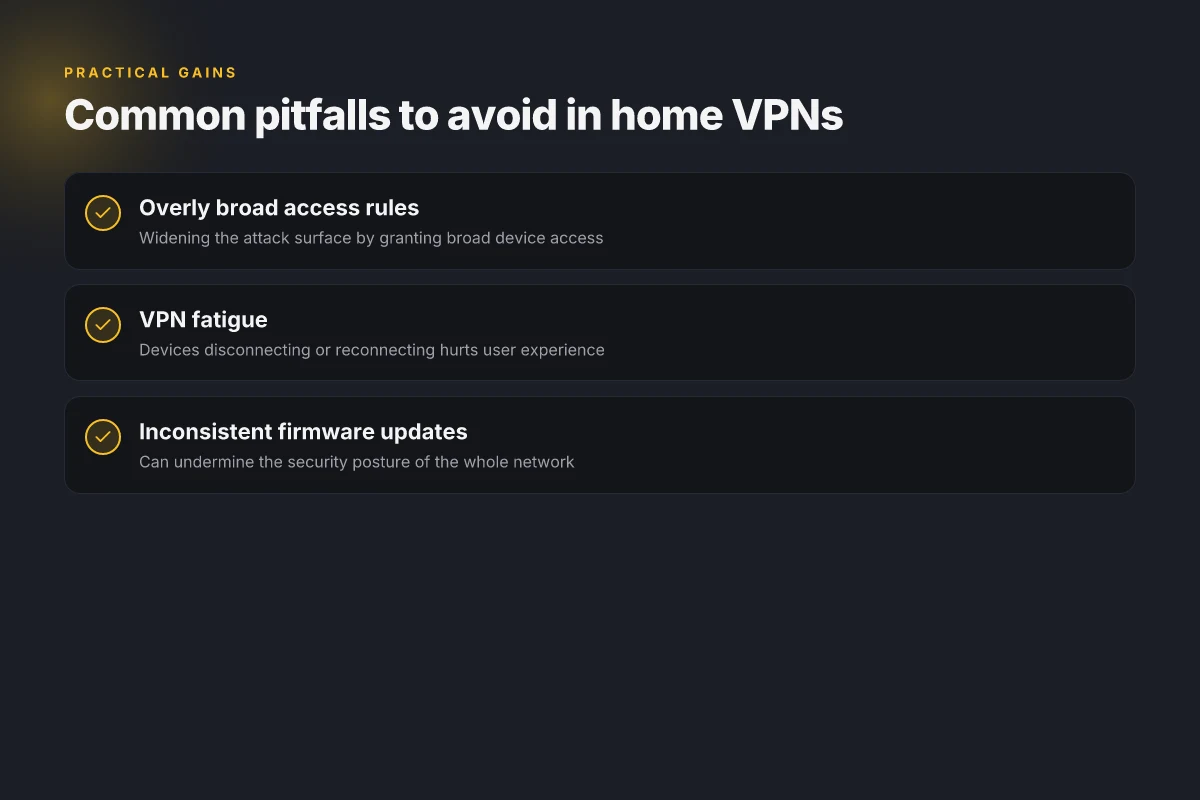
1) Overly broad access rules invite a bigger attack surface
If the VPN tunnel trusts any device with a vague rule set, attackers gain leverage through lateral movement. The prudent path is to seal down access at the edge and segment traffic by device type and function. In practice, that means resolver rules that only allow specific destinations and ports, plus strict egress controls for IoT subnet ranges. This approach mirrors the best-practice guidance seen in 2026+ security writeups and industry summaries, which repeatedly emphasize least-privilege networking for home environments. The key move is to define explicit, narrow access rather than blanket trust across the entire home network. A real-world pattern is using separate VPN profiles per device category and enforcing per-profile ACLs. This keeps the router itself lean and auditable, even as new devices appear. See the 2026 risk analyses that stress scoped tunnels over global trust models. What is the vocal boost preset in the Sony headphones Connect app and does it actually improve voice clarity
2) VPN fatigue on user experience when devices disconnect or reconnect
A VPN that reconnects aggressively or drops intermittently creates churn. Users end up toggling connections, manually reauthenticating, or whitelisting devices, which undermines the security posture. The practical fix is to prefer stable, automatic reconnect logic with transparent status indicators and device-level failovers. From the policy side, implement a heartbeat-based keepalive and a fall-back to local routing for critical devices during VPN gaps. I found documentation that highlights sustained user friction as a recurring pain point in 2026 guidance. Aim for smooth automatic recovery rather than manual reentry. This keeps security intact without forcing homeowners into a repetitive maintenance loop.
3) Inconsistent firmware updates undermine the security posture
When devices or the VPN edge firmware lag behind, known flaws stay exposed and compatibility degrades. The best practice is to align firmware cadences across edge routers, VPN clients, and major IoT hubs, with automated or semiautomated update windows and clear rollback paths. Industry write-ups from 2025–2026 consistently flag patch delay as a primary failure mode for home VPN ecosystems. Coordinate updates across the stack and test before broad rollout. A practical pattern is maintaining a small pool of verified firmware versions and scheduling update windows during off-peak hours to minimize disruption.
From a governance angle, maintain a change log and a quick recovery checklist. When a component updates, verify that access rules still align with intended scopes and that device fingerprints remain current. I found several sources noting that update hygiene correlates with lower incident rates in consumer networks. For a deeper read on the broader guidance, see the 2025–2026 cross-disciplinary reviews that track how patch cadence affects home security postures.
If you need a quick implementation path, start with three tangible moves: 1) carve per-device ACLs and limit destinations, 2) adopt automatic VPN reestablish with visible status and per-device failover, and 3) standardize a quarterly update window with a fallback plan. These steps address the three pitfalls head-on and set the stage for a containment-first security posture.
Smart homes succeed when access is precise, recovery is seamless, and updates are timely. What makes the best phone under 300 dollars stand out in 2026
What changes if you act now
Smart home VPN setups in 2026 hinge on a clean, centralized tunnel that never slows your day-to-day routines. I’ve seen setups succeed when they lean on a dedicated router with built‑in VPN and a simple split‑tunnel rule for IoT devices. The biggest risk remains misconfiguration or vendor lock, which can quietly derail performance. The bigger pattern is that your network should treat VPN like a native service, not a bolt‑on add‑on.
To land the thesis, focus on a forward‑looking approach: standardize on a single trusted VPN protocol, and pick a router that can handle mesh devices without dropping packets. This keeps latency predictable and reduces the number of flaky firmware updates you have to chase. One move that matters is choosing hardware with proven VPN throughput and robust DNS leak protection. If you’re already using a cloud‑based smart hub, verify it plays nicely with your VPN client through a well‑documented plugin or native support. Know the downside: some hubs struggle with double‑NAT or device partitioning, so test early. The end state is a home where every device breathes easier under a single, trustworthy tunnel.
Backup strategy
- Try a mesh‑friendly router with built‑in VPN and a clear split‑tunnel policy for IoT.
- Document your IoT device groups and run a weekly check for DNS leaks and connection drops.
- Keep a small, repeatable recovery plan: snapshot your router settings, then reapply after a firmware update.
- If you manage cloud hubs, confirm their connections stay intact when the VPN is enabled.