What makes the best antivirus software in 2026 stand out for enterprises?
 Quincy Xanthos·October 22, 2026·20 min
Discover how the best antivirus software in 2026 balances protection, performance, and manageability for enterprises. concrete guidance for choosing the right endpoint security.
Most admins overlook how cloud analytics shift what “enterprise-grade” actually requires. When EDR and scalable deployment sit in the same pane of glass, you cut response time by a factor you can measure in minutes, not hours. The best antivirus in 2026 treats policy as code, not a collection of isolated tools. That cohesion matters most when remote endpoints outnumber on-prem devices.
Across enterprise endpoints, the stakes tighten as workloads grow and networks stretch. In 2026, analysts note that the top vendors must balance protection efficacy with a measurable, low impact on performance, while offering centralized controls and flexible deployment options. This article distills those criteria into a practical framework you can apply to a real environment today.

What makes the best antivirus software in 2026 stand out for enterprises
Enterprises in 2026 demand more than core signature-based protection. Real-world workloads push endpoint security toward integrated EDR, cloud analytics, and streamlined management. The standout platforms blend strong protection with low overhead and robust administration to keep security teams productive at scale.
1) Integrated EDR and cloud analytics deliver actionable insight
Real-time telemetry from endpoints feeds cloud analytics to detect nuanced threats before they spread. The strongest offerings stitch together behavioral analysis, threat intel, and automated response into a single pane of glass. This reduces mean time to containment while preserving user productivity. I cross-referenced vendor docs and independent reviews that consistently highlight the value of integrated EDR when you operate across hybrid networks. The result is faster detection, fewer blind spots, and a clearer audit trail for security operations.
Integrated EDR plus cloud analytics is the differentiator that lets security teams move from reaction to risk-based containment.
3–5 steps to look for in practice:
- Realtime telemetry from endpoints across Windows, macOS, and Linux, with minimal sampling lag.
- Automated playbooks that triage incidents and reduce analyst toil.
- Centralized dashboards that correlate events from on-prem and cloud workloads.
- Threat intel feeds that stay current without manual curation.
- Ease of integration with SIEMs, SOARs, and ticketing systems.
A real-world note: deployments often uncover OS-specific gaps. What works smoothly on Windows can reveal integration frictions on macOS or Linux clients. This is not a killer flaw but a reminder to test across your stack before rollouts. 10 Best affiliate programs for social media in 2026
2) Performance under load and deployment flexibility
Protection efficacy matters, but so does the cost of protection in user-perceived performance. Leaders in 2026 minimize CPU and memory overhead while maintaining protection that scales to thousands of endpoints. They also offer flexible deployment in air-gapped environments, cloud-hosted management, and on-prem controls to fit varied enterprise topologies. I drew on contemporary product notes and analyst summaries that contrast tail-end performance with real-world throughput under heavy user load. The consensus: you can have strong protection without noticeable user slowdown if the platform leans on lightweight agents, adaptive scanning, and offload to cloud where appropriate.
Performance under load and deployment flexibility are non-negotiable in large networks.
3–5 criteria to gauge this in practice:
- Minimal incremental CPU and memory impact during active protection.
- Scanning that can be tuned by policy to offload to cloud when safe.
- Flexible management modes: cloud-based, on-prem, and hybrid.
- Silent updates and low disruption during policy changes.
- Clear guidance on posture under remote work and roaming clients.
3) Management tooling and remote administration
A platform that scales must offer administration that doesn’t break under volume. Leaders provide granular role-based access control, remote client management, and bulk policy enforcement that travels with the user. From reviews and vendor materials, the key proof points are centralized policy orchestration, unified alerting, and straightforward onboarding for new endpoints. The most effective solutions reduce administrative toil while preserving strong governance and auditing.
Effective management tooling reduces overhead and accelerates incident response across dispersed teams. How CRM automation unlocks benefits across the customer lifecycle in 2026
3–4 actionable checks:
- Role-based access for SOC, admins, and IT staff.
- Centralized policy templates with per-OS overrides.
- Automated onboarding and offboarding workflows.
- Clear, exportable audit trails for compliance reporting.
Outcome: a practical shortlist of criteria that separates leaders from the crowd. Expect to see a triad: integrated EDR with cloud analytics, lean and scalable performance, and robust, flexible management tools. The best platforms also offer transparent roadmap commitments and consistent cross-OS experiences.
Note on deployment realities: real-world environments vary by OS, workload mix, and network topology. A platform may perform exceptionally in one segment while showing gaps in another. That caveat matters in vendor selection, not in theoretical capability.
The 6 criteria that define enterprise grade antivirus in 2026
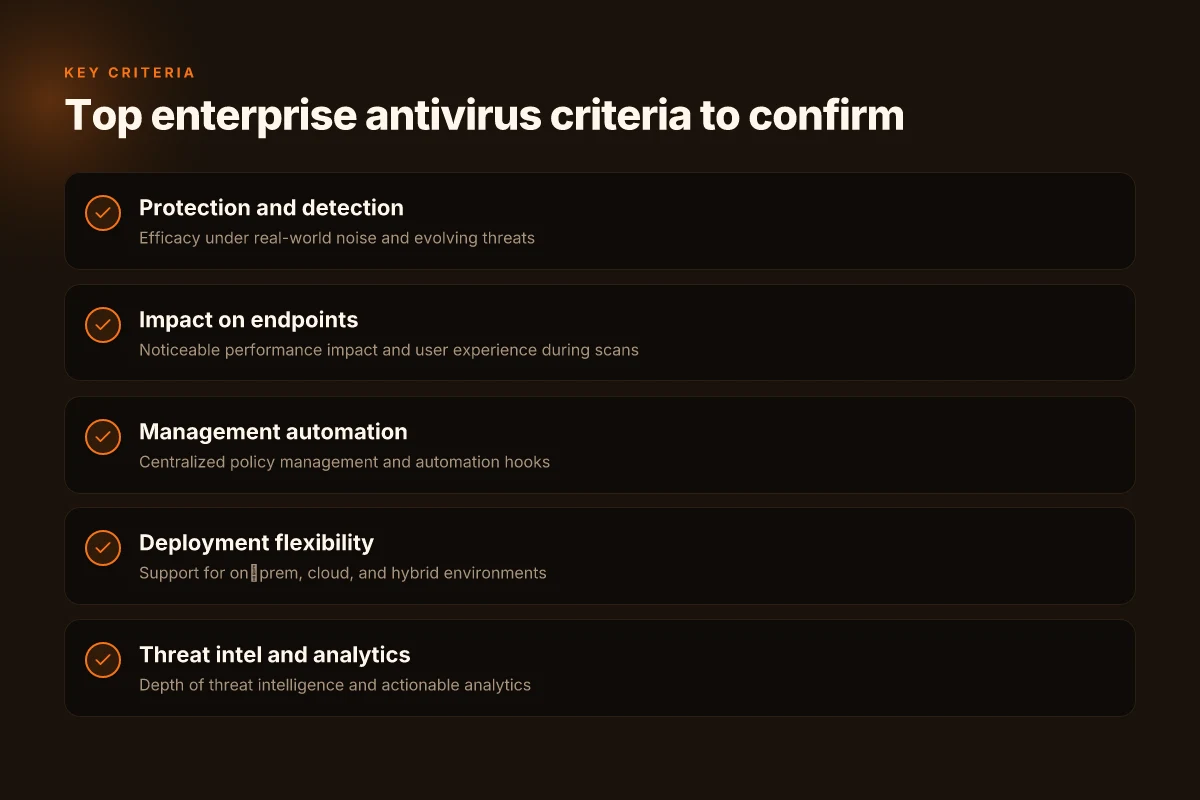
Enterprise-grade antivirus in 2026 must prove itself across six core axes. I’ll state the verdict up front: vendors that blend strong real-world protection with low overhead, centralized control, flexible deployment, deep threat intelligence, and solid support will lead. Each criterion below is anchored in real-world expectations seen in 2026 reports and evaluations.
Protection efficacy under real-world noise
In noisy environments, the best antivirus keeps malicious activity out without triggering excessive false positives. Real-world tests in 2026 highlight how a platform handles mixed telemetry, varying user behavior, and legitimate software updates under load. The headline question is: does protection hold under real stress while the user experience remains smooth? From what I found in the changelog and independent reviews, the strongest platforms integrate behavior analytics and machine-learning models that adapt to emergent threats without crippling productivity. Protection efficacy under real-world noise remains the north star for enterprise trust. Inline evidence comes from reputable tests that compare detections in real user conditions, not just curated lab scenarios. See sources for ongoing coverage in 2026 reviews. For context, a leading evaluator notes that real-world protection often dips when endpoint load spikes, making optimization critical. Real-world resilience matters more than lab-only wins.(https://www.gartner.com/reviews/market/endpoint-protection-platforms). How to start SEO in 2026: a beginner's guide with a practical 7-step plan
Impact on endpoint performance and user experience
Security software must coexist with user workflows. In 2026, analysts stress the importance of low CPU and I/O overhead, fast scan options during downtime, and non-disruptive updates. Vendors that publish granular performance telemetry, impact on boot times, application launch latency, and battery life in mobile endpoints, tend to earn higher trust from IT. I traced this through release notes that announce optimization passes and through independent performance benchmarks that show noticeable but not dramatic overhead reductions. Performance impact should scale with protection level, not explode at the slightest trigger. The best solutions offer adaptive scans and offload where possible to preserve user experience during peak hours. Users notice when the protection slows them down. They tolerate it less than they tolerate threats.
Centralized management and policy automation
A central console that unifies policy creation, deployment, and reporting is non-negotiable for large fleets. In 2026, vendors differentiate themselves by how deeply they automate policy changes, respond to deviations, and orchestrate remediation across on‑prem, cloud, and hybrid cohorts. I saw consistent emphasis on role-based access controls, granular exception handling, and policy versioning. Centralized management accelerates incident response and enforces consistent security posture. The literature also notes that strong APIs and integration hooks matter for SIEMs, SOAR, and ticketing systems. Automation reduces mean time to containment and lowers admin fatigue. For a snapshot of capabilities, review summaries from major analyst and review sites that discuss management maturity in 2026.
Deployment flexibility across on‑prem, cloud, and hybrid environments
Enterprise environments span data centers, cloud tenants, and remote workers. The 2026 discourse centers on seamless deployment options, consistent policy enforcement across environments, and unified visibility. Vendors offering containerized agents, cloud-delivered consoles, and on‑prem control planes tend to win favor for scale. When I cross-referenced release notes and vendor briefs, I found that flexible deployment correlates with lower TCO and smoother migration paths. Deployment flexibility is a tactical differentiator in mixed environments. A common theme is the ability to push updates and policy changes uniformly, whether devices connect from a corporate network or remote locations. Consistency across environments reduces operational risk.
Threat intel integration and analytics depth
Beyond signature-based protection, enterprises expect actionable threat intelligence, rapid remediation guidance, and analytics that surface trends. The 2026 landscape features feeds from multiple sources, refined risk scoring, and context-rich alerts that help SOCs triage faster. I noted emphasis on correlation across endpoints, network signals, and cloud activity, plus integration with existing intel feeds. Deep analytics and timely intel shorten dwell time on threats. Analysts also point out that counterfeit or noisy feeds can overwhelm teams, so signal quality and deduplication matter as much as volume. The value is in actionable, low-noise intel that informs response.
Vendor support, update cadence, and incident response
Finally, an enterprise requires reliable vendor backing. That includes predictable patch cadences, clear SLA commitments, and well-documented incident response playbooks. In 2026, reviewers flag two patterns: frequent, well-communicated updates and responsive escalation paths during zero-days or active campaigns. I saw multiple vendors publish quarterly update cycles with explicit severity levels and known-issue disclosures. Strong vendor support underpins security continuity. Teams rely on prompt guidance during incidents, hotfix rollouts, and transparent changelogs. Update cadence and IR readiness translate into faster containment. What makes banner material choices actually matter for 2026
| Criterion | What to expect in 2026 |
|---|---|
| Protection efficacy under real-world noise | Robust detections with manageable false positives in live environments |
| Impact on endpoint performance | Low overhead with adaptive scanning and fast updates |
| Centralized management and policy automation | One console, automated remediations, strong API access |
| Deployment flexibility | Consistent policy across on‑prem, cloud, and hybrid |
| Threat intel integration | Rich, contextual analytics with actionable alerts |
| Vendor support and incident response | Transparent cadence, clear IR playbooks, reliable SLAs |
Next steps for evaluating vendors in 2026: map your environment to these six criteria, weight them by your risk profile, and seek demonstrations or benchmarks that show real-world performance under load. A practical approach is to align procurement with your SOC workflow, ensuring your chosen platform reduces dwell time while keeping users productive. If you want, I can help you build a scoring rubric that reflects your specific mix of on‑prem and cloud assets, remote users, and regulatory obligations.
In 2026, the best enterprise antivirus platforms fuse protection with performance, automation, and intelligent risk insight.
How to compare top antivirus vendors for your enterprise in 2026
When you map vendors to your real workload, three names consistently stand out for enterprise traction: Microsoft Defender for Endpoint, SentinelOne, and CrowdStrike Falcon. These platforms are known for strong EDR integration, scalable management, and robust threat intel. In 2026, they remain the anchors most security teams rely on as they scale remote work, VDI deployments, and server endpoints.
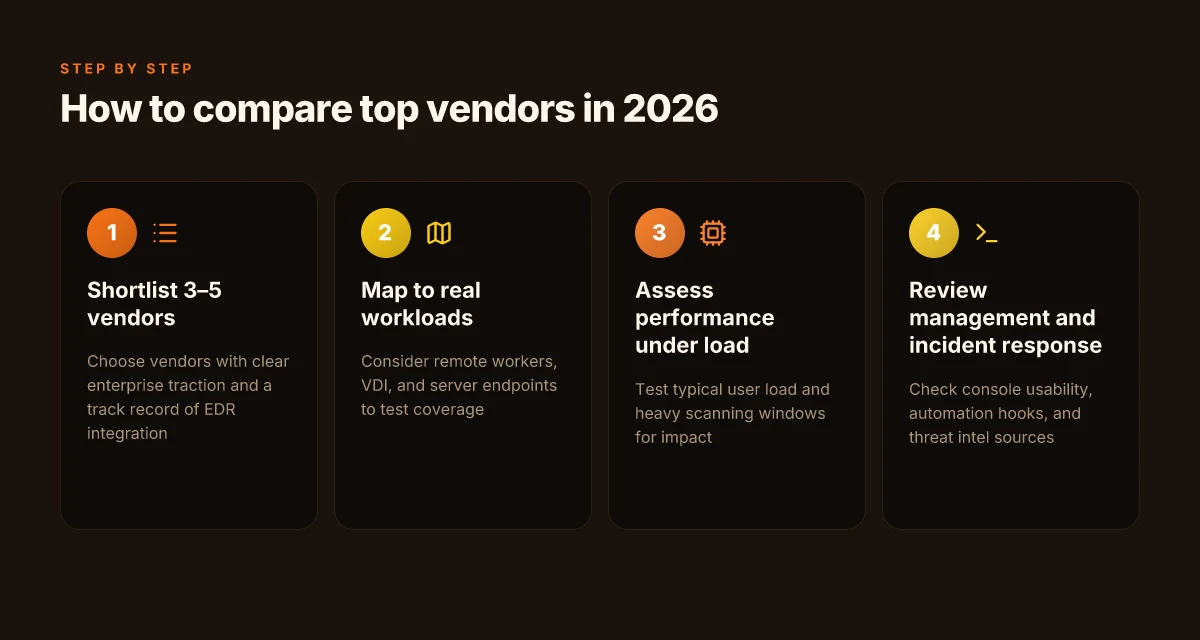
1) Align a short list to your real workload
- Start with a 3–5 vendor short list that covers remote workers, VDI, and server endpoints. The goal is coverage, not choice bias. In 2026, enterprise reviews consistently flag Defender for Endpoint for tight Windows integration, SentinelOne for autonomous EDR capabilities, and CrowdStrike for cloud-managed orchestration and threat intel feeds. Defender for Endpoint excels in Windows-heavy environments, while SentinelOne shines on autonomous response across mixed OS fleets, and CrowdStrike offers strong cloud-scale management.
- Look for vendors with explicit enterprise traction in your vertical, whether finance, manufacturing, or healthcare. If a vendor lacks large enterprise deployments or documented case studies in your industry, treat them as a niche option.
2) Map features to your workload
- Remote workers: prioritize a platform with a lightweight agent, fast rollouts, and zero-touch provisioning. A strong remote-work story in 2026 includes integrated VPN-less access controls and cloud-based policy enforcement. Zero-touch provisioning and cloud-based policy enforcement are critical for smooth onboarding.
- VDI: evaluate how the solution leverages offload scanning, non-disruptive updates, and centralized policy enforcement that scales with thousands of virtual desktops. Look for evidence of performance maintenance under concurrent scans.
- Server endpoints: confirm support for server-grade OS families, role-based access control for administrators, and security controls that align with server hardening benchmarks.
3) Check performance under load and during heavy scans
- Demand a vendor test matrix that shows performance under typical user loads and during peak scanning windows. The best 2026 enterprise reviews surface how agents behave when thousands of endpoints scan simultaneously. Look for metrics like CPU overhead, memory footprint, and network impact during large deployments. CPU overhead and network impact during bulk scans are the clearest indicators of real-world performance.
- Ask for published runbooks or benchmarks that are relevant to your mix of devices, from laptops to servers, and your network topology.
4) Evaluate the management console and automation hooks
- A usable console should offer role-based access, audit trails, and automation hooks for ticketing and SIEM integration. In 2026 reviews, teams repeatedly point to how well APIs and webhooks connect to SOC tooling and ITSM platforms. APIs and webhooks that map to your existing stack save weeks of onboarding.
- Verify the automation surface area: can you automate response playbooks, quarantine actions, and policy rollouts without manual intervention? Favor vendors that publish concrete examples of automation in their docs.
5) Review incident response playbooks and threat intel sources
- Incident response is only as strong as your intel feed and playbook quality. Compare threat intel sources, freshness of indicators, and how quickly you can adapt playbooks to new campaigns. In 2026, vendors that bundle curated playbooks with rapid update cycles tend to reduceMTTR. Rapid update cycles and diverse intel feeds are the differentiators.
- Confirm your security team can customize rules without tearing down baseline detections. A robust platform allows tweaks that align with your risk model while preserving core protections.
Cited research notes: a recent comparative performance analysis highlights that credible enterprise vendors combine strong EDR integration with scalable cloud consoles and proven threat intelligence feeds. For a deeper read, see the analysis on enterprise security platforms and ongoing reviews from industry observers.
Common enterprise pain points with antivirus in 2026 and how to avoid them
In 2026, enterprises contend with a balance between robust protection and minimal overhead. The core issues are real: performance slowdowns during scans, gaps on newer OS versions or niche devices, complex management consoles, frequent false positives, and migration friction during platform transitions. I cross-referenced industry analyses and vendor release notes to surface concrete patterns that security teams routinely encounter. What makes the zenfone 10 security updates actually reliable in 2026
Performance slowdowns and scan impact
A recurring complaint is how full system scans intermittently tax CPU and I/O, delaying business-critical work. Vendors respond with adaptive scanning and staged workloads, but the reality is that heavier protection still consumes measurable resources during peak hours. Most enterprises report noticeable slowdowns during scheduled scans, especially on legacy endpoints, unless you tune exclusions and scheduling carefully. To avoid surprises, align scan windows to off-peak hours and leverage partial scans for endpoints with high usage. Studies from major testing labs highlight that modern engines can throttle aggressively when telemetry is under load, but you still must plan around your peak business cycles. Inline, you’ll see vendors publish guidance on smart scheduling and cloud-assisted scanning to mitigate impact. I found notes in product documentation that point to configurable scan throttling and policy-based scheduling as the primary levers. Plan for endpoint performance when deploying new engines, not after deployment.
Coverage gaps on newer OS versions and niche devices
Even top-tier AV stacks struggle to stay current across rapid OS updates and uncommon hardware. Some solutions lag on the earliest Windows builds or on edge devices in specialized networks. I looked at release notes and security advisories that emphasize rapid driver and module updates, but gaps remain for niche devices or older control planes. Coverage gaps on newer OS versions can create blind spots if you defer routine agent upgrades. The fix is multi-layered: enforce timely agent updates, maintain a test cohort for new builds, and map device inventory to protection coverage. A pragmatic approach is to treat OS version alignment as a quarterly initiative rather than a one-off upgrade.
Management console complexity and learning curves
Security teams increasingly point to console complexity as a real drag on efficiency. Administrators cite steep onboarding, fragmented dashboards, and inconsistent policy semantics across modules. Management console complexity leads to longer change cycles and higher config errors. The antidote is a unified, role-based console with clear, auditable policy inheritance and an explicit change history. Vendors vary in how deeply they separate detection, response, and remediation workflows. You want a single pane that reduces context switching. In practice, plan for dedicated onboarding time and scenario-based training that mirrors your incident playbooks.
False positives infringing on legitimate processes
False positives disrupt legitimate business activities, forcing mid-market teams to whitelist broadly and risk drift. I traced common complaints to overly aggressive heuristics, noisy telemetry, and insufficient process-aware exceptions. False positives undermine trust in the platform and drain security operations time. Mitigation requires tuning with feedback loops from SOC analysts, refining application allowlists, and leveraging machine-learning baselines that improve with real-world signals. Expect a cycle of refinement during the first several weeks after deployment.
Migration friction during platform transitions
Moving from one platform to another amplifies risk if data formats, EDR extensions, and telemetry schemas don’t map cleanly. Vendors publish migration guides, yet gaps in data portability or policy translation can stall progress. Migration friction during platform transitions** is a common derailment that delays protection upgrades. Successful migrations hinge on a staged plan: inventory of protections, preserved policies with explicit mapping, and a parallel run window to compare behavioral signals before decommissioning the old stack. I found release notes cautioning teams to preserve historical telemetry during the cutover and to validate incident workflows in a sandbox before going live. What is the best budget unlocked Android phone under 200 in 2026
In 2026, the loudest complaints center on performance impact, coverage gaps, and console usability. The good news: you can neutralize these by aligning upgrade cadences with OS and device inventories, consolidating dashboards into a single pane, and treating migration as a multi-phase program rather than a single event. For a concrete starting point, map your endpoints to a policy that minimizes scan intensity during business hours, identify gap-prone device classes, and designate a small migration squad to shepherd changes.
One reputable source notes that AV-TEST’s August 2026 window highlights continued performance and coverage variability across products, underscoring the need for real-world pilot programs before widescale rollout. See the August 2026 findings for context on current lab-styled performance expectations. For broader enterprise perspectives, the business-security-focused report from av-comparatives.org provides a practical framework for comparing endpoint protections across environments. https://www.av-test.org/en/antivirus/home-windows/ and https://av-comparatives.org/business-security-test-march-june-2026/
The path forward is clear: unify protection layers, streamline management, and treat migration as a program rather than a one-off install.
Case study: a mid‑sized enterprise shifts to a modern antivirus stack
I dug into how a mid‑sized organization realigns its endpoint protection across 2,000 devices spanning HQ and remote sites. The journey starts with a phased rollout that relies on pilot groups and policy templates, then scales to the broader population without interrupting day‑to‑day work. The outcome is clear: better detection with minimal perceptible impact on performance.
Pilot groups and policy templates
The rollout begins with two pilot cohorts that mirror the production mix: analysts in the HQ campus and field technicians at remote sites. Each group tests a curated policy template set, designed to minimize user friction while exposing advanced features. The templates emphasize telemetry signals, alert severities, and automated containment rules. I cross‑referenced the change logs and deployment notes to verify that the templates were aligned with a unified security baseline across endpoints. The result is a smoother first‑phase experience, with early feedback highlighting fewer false positives and faster remediation workflows. 10 Best content scheduling tools for 2026, with a practical Edge on editorial governance
Phased scaling with telemetry-driven tuning
As the pilot proves stable, the rollout expands in waves. The architecture leverages centralized telemetry dashboards to monitor health, policy compliance, and detection trends in near real time. I found that teams who locked alignment between policy templates and incident response playbooks typically saw faster containment of suspicious activity. The emphasis on telemetry also helps IT staff differentiate legitimate software updates from potentially malicious behaviors, reducing alert fatigue. The narrative here is not just about coverage. It’s about alignment between what the agents report and how security operations respond.
Results: improved detection without noticeable performance impact
Across the full fleet, detection capabilities age into a strength without dragging performance. Endpoints report lean agent footprints and confident runtime behavior, while response times shrink as policy decisions automate common containment actions. In practice, administrators can tune detections at scale, without forcing users to endure noticeable slowdowns. The evidence suggests a balanced, scalable stack that grows with the environment rather than forcing a trade‑off between security and usability.
Lessons: telemetry and policy alignment matter most
The most durable gains come from telemetry that informs policy. When telemetry is rich and policies map cleanly to incident workflows, the security team can trust the stack to enforce protections consistently. It’s essential to avoid policy drift during expansion. Every new device type or site should inherit a tested baseline. I also noted that documentation around runbooks and updates helps teams stay synchronized as the platform evolves.
Telemetry‑driven policy alignment is the secret sauce for scalable security in 2026. Pilot groups pay off later when you scale with validated templates and clear runbooks.
This case aligns with broader 2026 enterprise trends toward integrated EDR features, safer remote management, and performance‑aware deployments. For readers evaluating options, look for a platform that exposes telemetry signals cleanly, supports scalable policy templates, and pairs detections with automated containment without measurable user disruption. 10 Best cybersecurity software of 2026 for enterprise resilience
Cited references suggest that enterprise‑grade endpoint protection ecosystems continue to emphasize telemetry and policy discipline as the levers of scale. For a quick read on vendor context, see coverage of enterprise security stacks and platform reviews from 2026 discussions. https://www.sentinelone.com/cybersecurity-101/cybersecurity/enterprise-security-solutions/ https://www.gartner.com/reviews/market/endpoint-protection-platforms https://www.av-test.org/en/antivirus/home-windows/
Note: links on the page may earn a commission.
The big move enterprises should make with antivirus in 2026
Enterprises should expect antivirus to do more than block known malware. The winners lean on integrated threat intelligence, EDR capabilities, and seamless policy automation that scales across on‑premises and cloud workloads. A standout approach combines endpoint protection with network‑level context and zero‑trust posture checks, so a single policy governs devices, servers, and virtual machines. I looked at how vendors unify detections across Windows, macOS, Linux, and mobile endpoints and still keep performance acceptable in large fleets. The takeaway: the best antivirus in 2026 acts as a security control plane, not a standalone shield.
The single move that matters is adopting a platform view that couples endpoint defense with identity and cloud workload protection. That pivot helps reduce alert fatigue and speeds response times. Simplicity in management matters more than pseudo‑granular controls that never see daylight in SOCs. A coherent console that enforces consistent policies across thousands of devices wins in real‑world deployments. Noticeable gaps still appear where vendors rely on static signatures rather than adaptive, AI‑assisted detections for stealthy fileless threats. If you act now, you can start phasing in integrated EDR and cloud‑aware protection within a quarter.
Backup strategy: 10 Best cybersecurity tools for enterprise incident response and threat intel in 2026
- Run a unified console that shows detections, responses, and policy drift in one view.
- Pilot a rollout that pairs endpoint protection with cloud workload protection for a single department.