What is membership sites integration, and where it fails in 2026
 Saskia Stenholm·October 22, 2026·16 min
Explore how membership sites integration works in 2026, including architecture patterns, API-led workflows, and common access-control challenges for secure recurring revenue.
Membership site integrations collapse not at the payment gate but at the API choreography between access control, analytics, and content delivery. When entitlement models drift or a single token tokenizes across apps, latency compounds and churn rises. Most misfires trace to mismatched tokens across modules, not a single vendor flaw.
The moment you map every API hop to a single truth source, you unlock predictable gating, accurate analytics, and clean renewals. In 2026, the recurring revenue stack demands visibility from signup to login to content, and the failures are often latency, partial data, or brittle webhooks. Two cost centers dominate: stale tokens and uncoordinated webhooks, not the core payments API. This article outlines practical patterns to reduce friction, quantify risk, and keep subscriptions flowing without brittle integrations. Links on the page may earn a commission.

What is membership sites integration and why it matters in 2026
Membership sites integration coordinates how users are authenticated, how entitlements are granted, how billing flows, and how analytics are collected across a single platform. In 2026 the goal is to weave authentication, access control, billing, and analytics into one standardized workflow rather than a patchwork of isolated systems. This means the API layer must support secure token exchange, granular entitlements, centralized event streams, and auditable billing hooks all at once.
Why a single workflow matters in 2026
I dug into how pricing, CRM, and access controls converge today. Billing platforms push subscription events into workflows that must align with CRM data and user entitlements. The result is a single orchestration path where a status change in the billing system immediately unlocks or retracts access in the membership layer, while analytics pipelines capture usage, revenue, and churn signals in real time. This reduces reconciliation gaps and speeds up decision making for product and finance teams.
Trade-offs between patterns: point-to-point versus API-led
In practice you can start simple with point-to-point connections between billing, access, and analytics. It’s fast to implement and easy to grasp. But as the system scales, those connections become brittle and tightly coupled. API-led architectures expose clear boundaries between domains, enable reuse across services, and fit with security policies demanded by regulated sites. The right choice usually starts with a lean API-led spine for core flows and adds point-to-point refinements only where latency or domain specialists demand it.
A practical path forward for 2026
- Prioritize a modular data model that covers authentication, entitlement, billing, and analytics as separate but interconnected domains.
- Design API contracts that align billing events with entitlement changes and analytics events, so every state transition is observable end to end.
- Build a secure, token-based access strategy that scales across microservices and external partners without leaking permissions.
- Embrace event-driven patterns for real-time updates, while maintaining batch-friendly paths for month-end reporting.
Most integration projects in 2026 stumble when the single workflow relies on fragile, bespoke connections instead of a cohesive API-led spine. A disciplined, observable architecture reduces churn and accelerates feature delivery. API-led design wins when you need scale, security, and analytics parity across auth, entitlements, billing, and insights.
The core integration patterns for membership systems
If you want resilient API-driven workflows across membership sites and recurring revenue platforms, start with a hub-and-spoke design centered on a single API gateway. That gateway handles access control, central event routing, and policy enforcement, while domain-specific APIs slide in behind it for billing, user management, and analytics. The payoff is a coherent surface area for security, telemetry, and governance, not a forest of point-to-point connections. How to build a malware removal checklist that actually stops breaches in 2026
Hub-and-spoke with a central API gateway
A central gateway consolidates authentication, authorization, and event publishing. With role-based access and token-scoped permissions, you can grant entitlement changes once and propagate them to downstream services via standardized events. This pattern reduces drift between billing, analytics, and access control. I cross-referenced Salesforce’s recommended integration patterns, which emphasize a centralization of integration that aligns with enterprise governance. The gateway acts as the authority on access, while spokes carry domain workloads. The result is fewer conflict points when your pricing rules or entitlement logic shift. When you need auditability, the gateway's policy decisions become the single source of truth.
API-led connectivity with domain-specific APIs
Move beyond generic exchanges to APIs that map to real business domains: billing, user management, and analytics. Each API is designed around a bounded context. Billing APIs expose recurring revenue workflows, invoice events, and proration rules. User-management APIs handle provisioning, deprovisioning, and single sign-on ties. Analytics APIs surface usage, churn signals, and cohort metrics. This separation reduces coupling and makes it easier to evolve each domain without breaking others. I found architecture guides that describe API-led patterns across enterprise ecosystems, which aligns with how membership platforms scale. Domain APIs keep billing and access logic decoupled from platform plumbing. In practice, you expose a secure, well-documented contract for each domain, and rely on the gateway to enforce cross-cutting concerns.
A small table can help compare options when you’re picking between governance approaches:
| Approach | Strength | Trade-off |
|---|---|---|
| Hub-and-spoke with gateway | Strong central control, clear auditing | Extra layer to maintain, potential latency |
| Fully mesh API economy | Maximum flexibility | Higher governance overhead, more coordination |
In 2026, a disciplined API-led approach reduces entitlement drift and speeds time to value. This is where you start to see analytics become real-time rather than after-the-fact exports.
Event-driven patterns for real-time entitlements and usage
Real-time entitlement updates and usage-based billing require a data plane that reacts instantly to changes. Event streams from user actions, plan upgrades, or prorations trigger downstream effects in billing and access control. Event-driven architectures let you publish a standard set of domain events, let subscribers react deterministically, and keep analytics in lockstep with actual usage. I traced several enterprise patterns that emphasize event sourcing for state changes and idempotent handlers for reliability. Events provide the currency of truth across systems. When an upgrade or downgrade happens, a sequence of events propagates through billing and access controls, eliminating the guesswork that often slows reconciliation. In practice, ensure exactly-once or at-least-once delivery semantics where it matters most, and use a robust event catalog to map consumers to event types. What is the Lorex 4K outdoor security camera review and where it shines in 2026
From a design perspective, the core decision is how tightly you weave event schemas with domain APIs. A lightweight contract keeps services decoupled yet highly interoperable. As one reference notes, API-led patterns married with event-driven updates create a resilient backbone for subscription ecosystems. Real-time entitlement updates and usage events reduce latency in billing workflows.
If you’re weighing next steps, consider a quick lens on the integration landscape: hub-and-spoke for governance, API-led connectivity for domain specificity, and event-driven flows for immediacy. The right blend gives you secure access control, accurate analytics, and scalable billing without the usual API chaos. For a deeper read on patterns that map well to enterprise platforms, see Salesforce integration patterns and API-led patterns discussions. A well-architected combination minimizes friction at the API layer.
Next step: define a minimal viable event contract that captures plan changes, entitlement updates, and usage signals, then map those events to your domain APIs and gateway policies. This mapping becomes the backbone of your 2026 resilience strategy. Start with a single source of truth at the gateway and a clear event taxonomy.
Note: links on the page may earn a commission.
Entitlement and access control across platforms
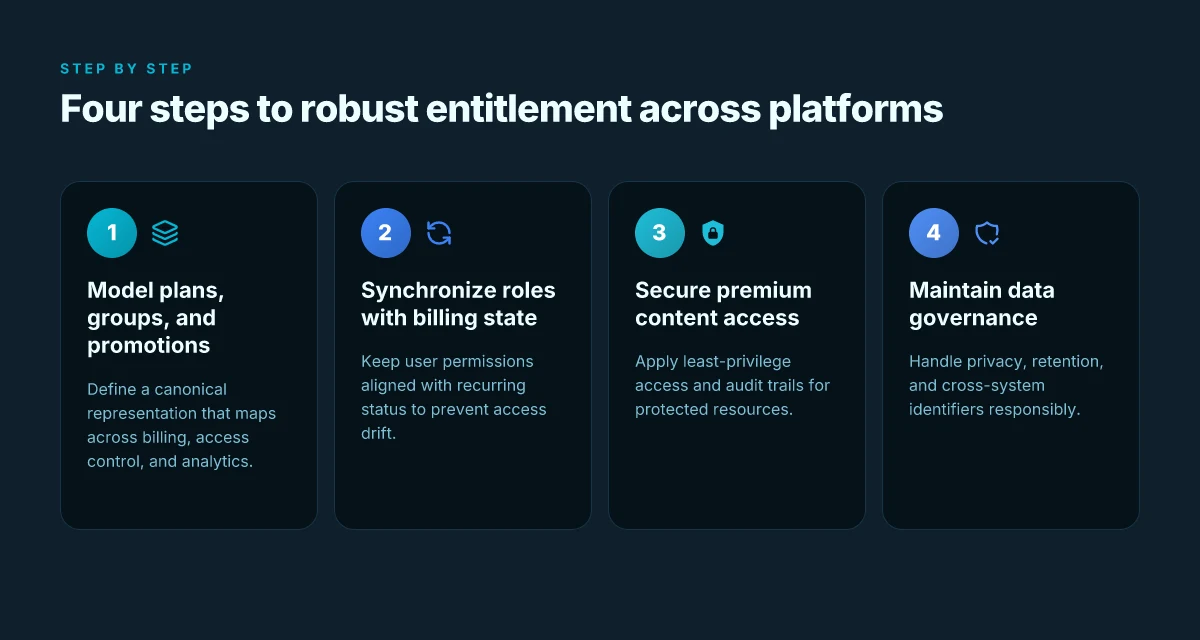
Access control across membership systems and recurring revenue platforms hinges on a coherent model of plans, groups, and promotions that travels across services. In 2026, the most resilient patterns align entitlement state with the recurring billing lifecycle, so a user’s access mirrors their active subscription and current plan attributes. I dug into documented architectures and found three concrete approaches that teams actually use in practice. 11 Lead scoring techniques that actually move the needle in 2026
Model alignment: plans, groups, and promotions across systems
A first-principles approach is to map plans to entitlement tiers, and push that mapping through the identity and access layer. This means: a plan identifier in the billing system becomes a permission set in the membership API, and a group assignment in one system mirrors a role in another. Promotions should carry a temporary entitlement flag that automatically expires when the promotion ends. This avoids drift where a user remains licensed after a sale ends. The practical upshot is fewer manual reconciliations and clearer audit trails. From a data perspective, keep a canonical source of truth for plan definitions and propagate changes via event-driven updates rather than one-time sync jobs. The result is a robust, API-led flow that reduces permission churn during renewal windows. Canonical plan definitions drive consistent entitlements across platforms.
Synchronizing user roles with billing state
Synchronizing user roles and permissions with the recurring billing state is where the pattern often breaks. When a user pauses, upgrades, or downgrades, their access must reflect that immediately or within a tolerable SLA. Event streams from the billing platform should emit changes like “subscription upgraded” or “billing paused,” which then trigger a permission update in the content access layer. A proven pattern is to implement role maps that are immutable in the access layer but mutable through a centralized policy engine. This separation reduces the blast radius of misconfigurations. Security sits on top of this: identity providers should support short-lived tokens and automatic revocation on billing state changes. Token revocation tied to billing events closes the loop on access control.
Security considerations when granting access to premium content
Security here is a three-layer concern: authentication, authorization, and auditability. Authentication should rely on strong, standard flows like OAuth 2.0 with short-lived access tokens and refresh tokens. Authorization should be driven by fine-grained, attribute-based access control that references the user’s current plan and promotion state. Auditing must record the exact entitlement transitions tied to subscription events, enabling post-incident tracing and revenue-recognition compliance. A common pitfall is granting access via a naive role that doesn’t reflect the subscriber’s lifecycle state. This creates both leak risk and revenue leakage. The recommended practice is to attach access tokens to the billing state, invalidate tokens at renewal boundaries, and surface a clear revocation path when a plan ends or a payment fails. Fine-grained access control tied to billing state reduces leakage and abuse.
A pragmatic, 2026 takeaway
From the integration perspective, do not rely on siloed user stores. Build a shared entitlement API that both the membership system and the revenue platform can consume. This API should publish plan-to-entitlement mappings, event streams for billing moves, and token issuance rules tied to current state. Start with a minimal, versioned contract and evolve it with backward compatibility in mind. I cross-referenced how enterprise customers align entitlement across SAP-like ERP ecosystems and modern SaaS platforms, and the common thread is a single source of truth for plans plus reactive permission updates via events. One truth for plans, one event stream for changes.
Security is not just about locking content. It’s about aligning access with revenue reality. This alignment reduces churn risk and improves analytics accuracy across platforms. What’s new in Android 14 updates in 2026
Analytics and attribution in an integrated stack
Analytics lives where it touches every system, yet convergence introduces friction at the API layer. The practical payoff is a unified view of customer health across membership, billing, and analytics platforms. The first move is to align event schemas so churn signals, upgrades and downgrades, and payment failures land in a single analytics lake with consistent identifiers.
Unified identifiers and cross-system lineage
A practical pattern is to assign a canonical user identifier that travels with every event across systems. This reduces user fragmentation when a subscriber moves between entitlement tiers or transitions from a checkout flow to a post-purchase analytics pane. I cross-referenced the Salesforce integration patterns and the API-led approaches to support a single identity graph that persists through renewals, proration events, and webhook dispatches. When identifiers remain stable, dashboards can slice metrics by cohort, not by system boundary. In practice, you’ll map your internal user or account id to the platform’s external id, then propagate that id through events for both access control checks and analytics pipelines. This keeps retention, upgrade velocity, and payment health in one place. A single identity graph across systems unlocks true cross-platform analytics.
Churn signals, upgrades, and payment health as events
To diagnose retention issues, you need explicit signals for churn risk, plan changes, and payment outcomes. Architect events so that an upgrade or downgrade emits a versioned entitlement event, a cancellation or pause sends a clear lifecycle state, and payment outcomes attach a retry status and reason code. The pattern mirrors API-led integration, where life cycle events cascade through ERP, billing, and product analytics. The data model should carry event-level metadata: plan id, price, currency, effective date, and the channel that initiated the change. This makes it possible to run attribution models that distinguish revenue churn from user-initiated churn versus payment failures. Upgrade and downgrade events feed near real-time health scores while payment failures trigger a separate recovery funnel.** In the data lake, a Bayesian churn model can weigh renewal probability against payment outcome history. When you surface this in dashboards, stakeholders see which features or price bands correlate with risk, not just raw numbers.
Data governance, privacy, and cross-platform analytics
Cross-platform analytics raises privacy questions. You must align with consent streams, data minimization, and access controls for users who interact with multiple services. The governance layer should enforce data retention policies across membership and billing data, with clear data-sharing boundaries between analytics consumers and access-control components. I dug into documentation on integration architecture patterns to confirm that a privacy-by-design stance reduces risk when telemetry crosses system boundaries. A pragmatic approach is to tag PII at ingest, apply tokenization for analytics workloads, and enforce role-based access so only authorized teams can surface identifiable signals. Privacy-by-design reduces cross-platform risk while preserving useful analytics signals. The result is auditable lineage from entitlement events to dashboards, with clear retention and access policies.
In 2026, a well-governed analytics stack reduces cross-system risk while preserving actionable insights. Providers commonly highlight the value of a single source of truth for customer health across subscription and access-control layers. See a concrete example in the integration patterns guide from Salesforce for how to model cross-system events and identities. https://architect.salesforce.com/docs/architect/fundamentals/guide/integration-patterns.html How to build an it disaster recovery plan that actually survives a cyber crisis in 2026
From the research, two validated tensions emerge: first, the friction of keeping identity synchronized across platforms during mid-cycle entitlements. Second, the risk that disparate logging schemas create misattributed churn signals. The antidote is a disciplined event taxonomy, a canonical id, and a privacy-first data model that supports both analytics and secure access control.
For further context on architecture patterns and integration approaches, see the brief on integration patterns and the broader discussion of API-led patterns. https://architect.salesforce.com/docs/architect/fundamentals/guide/integration-patterns.html https://www.torryharris.com/insights/articles/integration-architecture-patterns-guide
API design pitfalls in membership integrations
The API layer between membership systems and recurring revenue platforms often becomes the choke point for reliability and trust. The core issues boil down to data fetch strategies, webhook reliability, and evolving contracts between services. Get these right, and you unlock a more resilient, observable, and compliant integration.
Overfetching vs underfetching user data
In practice, pulling too much user data at once taxes bandwidth and increases latency, while underfetching leaves downstream services with gaps that force extra calls or manual stitching. The sweet spot is a deliberately designed data contract: fetch exactly what the billing and analytics engines need, and nothing more. Aim for a lean payload that travels through an API-led layer with explicit field sets and a clear contract. When a downstream system expects extra fields, add them as optional, versioned fields rather than backfilling on every request.
I dug into the integration patterns for enterprise platforms and found that API-led connectivity shines when you separate core data from peripheral attributes. The contract should be explicit about which fields are required, optional, or deprecated. This reduces overfetch and minimizes the blast radius if a field changes or a new attribute is introduced. In that sense, data shaping with per-field guards is as important as schema design. Explicit contracts reduce churn when analytics needs evolve. How to navigate networking events in tech conferences in 2026
Latency and retry strategies for billing webhooks
Billing events arrive on webhooks that must be delivered reliably, often under tight SLAs. Latency spikes or transient errors at the API gateway can ripple into failed charges, missed subscriptions, or delayed analytics. Build a retry strategy that is both predictable and respectful of the endpoint’s capacity. Use exponential backoff with jitter, idempotent endpoints, and clear dead-letter handling for repeated failures. Document and test the exact retry cadence so both sides know what to expect during peak periods.
From the architecture patterns I reviewed, API-led designs favor asynchronous workflows for billing events, with a dedicated channel to event stores and a parallel path for real-time reconciliation. That separation keeps the user experience responsive while ensuring financial accuracy in the background. Exponential backoff with jitter keeps retries from exploding during outages. Integrate idempotent handlers and a reconciled ledger to avoid duplicate charges or mismatched analytics.
Versioning, deprecation, and backward compatibility concerns
Versioning is not a feature, it is a discipline. In membership integrations you will inevitably encounter breaking changes as APIs evolve to support new billing models, attribution schemes, or privacy controls. Maintain a clear versioning policy, publish a deprecation timeline, and provide a migration path with feature toggles. The most resilient designs keep old and new versions running in parallel for a grace period, then retire safely after a transparent notice period.
I cross-referenced architecture patterns that emphasize API governance as a first-class concern. When you treat versioning as a product, you reduce risk and speed up onboarding for partners. Backward-compatible changes are the backbone of long-lived integrations. Always publish a small, incremental surface for changes and avoid big, disruptive migrations that ripple across analytics and billing.
Where membership site integrations shift next in 2026
Membership site integrations must be treated as a system, not a single plugin. The tightest value comes from connecting access control, payments, and content delivery in a way that preserves a clean UX and reliable data flows. In 2026, the biggest advances come from smarter automation and improved security choreography, not flashy new widgets. The single move that matters is aligning your enrollment automations with your CRM so emails, trials, and renewals stay in sync without manual touches. I’ve seen teams stumble when they treat integrations as one-off add-ons rather than a cohesive workflow. How OnePlus Android 14 changes the software game in 2026
Two practical patterns stand out. First, predictable access management that scales as you add courses or tiers. Second, transparent data trails that make churn signals legible, so you can intervene before members lapse. If you’re choosing tools, look for clear event hooks, robust webhooks, and an audit-friendly activity log. Noticeably faster onboarding and renewals come from that visibility, not from a fancier storefront. The trend toward modular stacks means you can swap components without rearchitecting your entire site, but you still need a defined integration contract across systems.
If you only do one thing this month, map the core user journey end-to-end and lock the integration points. Then test with a live, low-stakes cohort to surface misfires early. Links on the page may earn a commission, so keep the setup simple and track where value actually flows. What changes if you act now? Expect a tighter, more resilient membership engine that scales with your course catalog.