What makes two factor authentication stronger in 2026
 Mateus Ashworth·October 22, 2026·15 min
Explore how two factor authentication evolved in 2026, the trade-offs, and practical steps to deploy stronger MFA across organizations.
Context-aware and passwordless MFA are outpacing static tokens, and the shift is accelerating how we measure risk. In 2026, the strongest deployments lean on hardware keys, platform authenticators, and adaptive prompts that respond to device state, user behavior, and network risk.
Context paragraph: The stakes are practical: phishing-resistant methods cut exposure where passwords fail most. This piece surveys why context, not cadence, matters for admins, and how accessibility gaps shape adoption. Expect concrete guidance on policy tuning, risk signals, and what a minimal, compliant MFA stack looks like when passwordless options are the default. The payoff is fewer tickets and clearer verification steps for admins to escalate when risk signals rise. Links on this page may earn a commission.

What is two factor authentication in 2026 and why it matters for security
Two-factor authentication (MFA) blends at least two independent factors to verify a user. The core model blends something you know (a password), something you have (a hardware token or a mobile push, for example), and something you are (biometrics). Modern MFA also leans on risk-based triggers and adaptive flows: if a login comes from an unfamiliar device or location, the system can demand a higher assurance factor or a step in-line with context. The best MFA models balance security with usability by layering adaptive steps rather than forcing a single, brittle barrier.
What makes MFA worth keeping, even as password resilience evolves? Passwords remain a common attack surface, and MFA adds a multi-layer bar that protects accounts when credentials leak. In practice, organizations can reduce phishing risk, limit lateral movement after a credential leak, and improve auditability through stronger sign-in signals. I cross-referenced reviews and standards that emphasize risk-aware workflows and flexible policy controls, not just token counts. MFA remains a cornerstone because it shifts the security requirement from password strength alone to context-aware verification.
Across industries, three trends shape MFA adoption in 2026. First, passwordless approaches are rising, with phishing-resistant methods that replace static secrets with hardware-bound or device-based proofs. Second, there is a push toward context-aware, risk-based authentication that adds friction only when anomalies occur. Third, accessibility and usability gaps persist. Vendors and enterprises grapple with inclusive design to reduce friction for users with disabilities, while still preserving strong assurance. In this landscape, organizations tend to favor models that combine biometric or token-based proofs with adaptive prompts and clear recovery paths. Passwordless and risk-based MFA are no longer niche options. They are shaping the baseline for enterprise security.
From what I found in the documentation and reviews, expect MFA to evolve from fixed tokens to flows that respond to real-time context. When a user enters a familiar device in a known location, verification may stay lightweight. If risk flags appear, the system can require a stronger factor or a short-lived credential. This shift helps teams maintain productivity while improving security posture. Context-aware MFA is the pragmatic path forward for 2026.
In practice, organizations should pursue a concrete path: map access across critical systems, choose a flexible policy engine that supports risk-based prompts, deploy phishing-resistant factors, and ensure accessible design for all users. The literature consistently notes that successful MFA programs deploy layered signals, clear user guidance, and robust recovery options. A balanced, adaptable MFA posture reduces friction while raising assurance. Inline citation to an authoritative overview How to switch code editors and IDEs in 2026 without losing productivity
The evolving factors: what counts as a factor in modern two factor authentication
Two-factor authentication now rests on three canonical pillars. The classic trio, something you know, something you have, something you are, still anchors many deployments, but the emphasis is shifting. Passwords remain common as the “something you know,” yet passwordless and biometric factors are rising to prominence as either primary checks or strong secondary verifications. I dug into recent practitioner and standards material and found a clear move toward reducing reliance on static secrets while increasing the trust that context can provide. Passwordless and biometric checks are increasingly deployed as primary or secondary factors, reshaping what qualifies as a usable X factor.
Subtle but powerful are contextual signals that govern whether a factor should be trusted. Device posture, which includes enrolled certificates, firmware health, and security controls, often acts as a gatekeeper. Network reputation, such as known-good IP ranges or flagged anomalous routing, informs risk, and user behavior analytics can trigger step-up checks when patterns look off. In practice, this means authentication is no longer a single event but a negotiated risk decision. Contextual signals like device posture, network reputation, and user behavior enable adaptive authentication that reduces friction while tightening protection.
Open-system ecosystems demonstrate how these elements combine. Many modern MFA models blend a passwordless start with a biometric verifier and then layer contextual checks before granting access. For instance, a user might authenticate with a biometric on a trusted device, but if the device is unrecognized or the user is attempting access from an unfamiliar network, a stronger second factor or step-up challenge kicks in. The result is fewer false positives and a more resilient defense against phishing and credential stuffing. Contextual checks reduce reliance on static passwords by gating access with adaptive prompts when risk rises.
To help readers compare options, here is quick framing of how factors can align in 2026. The following table contrasts three common patterns:
| pattern | core factor mix | typical user impact | notable caveats |
|---|---|---|---|
| passwordless primary | biometrics or possession-based credential + platform attestation | lower friction, faster sign-ins | reliance on biometric privacy and device trust; enrollment burden |
| biometric primary with fallback | biometric first, with a cryptographic token as backup | strong resilience to credential theft | needs robust device security; accessibility concerns for some users |
| contextual adaptive MFA | passwordless or password-based with device posture + network context | tiered access with risk-based prompts | complexity in policy management; requires telemetry across devices |
One concrete takeaway is that a strong 2026 posture blends friction-aware usability with deeper risk signals. I cross-referenced guidance in healthcare authentication reviews and enterprise MFA discussions, which consistently note the value of reducing password exposure while preserving accessibility for all users. Adaptive MFA guided by device posture and network reputation tends to deliver both security gains and better user satisfaction. What makes Microsoft 365 Business Basic a smarter choice for small teams in 2026
Next steps for practitioners are practical and directional. Start by mapping current factors to a risk model: identify which factors you already collect, where gaps exist, and how you would escalate authentication in higher-risk scenarios. Align policy with user cohorts and device refresh cycles so the experience remains fluent rather than punitive. Map risk signals to your policy so users encounter minimal friction on low risk and stronger checks when risk spikes.
Note: links on this page may earn a commission for referrals.
Risk-based and adaptive MFA: when to tighten the grip without breaking the user
Adaptive policies turn up the verification when the signal says risk is high. In practice this means policy engines watch for anomalies in location, device posture, and behavior patterns, and then trigger an extra check without forcing every user to prove themselves again. I cross-referenced policy guides and recent reviews that discuss how to map signals into step-up prompts and how to avoid treating every login as a red-flag. The result is a posture that defers friction to when it actually improves risk posture, not as a default burden.
Calibrating friction with tiered access
When risk signals rise, your system should escalate authentication level in a controlled, predictable way. A common model uses tiered access: low-risk operations stay on a baseline factor, while sensitive actions demand step-up verification such as a second factor or biometric re-authentication. This approach keeps routine tasks flowing while preserving defense-in-depth for high-stakes actions. The guidance I reviewed emphasizes aligning step-up thresholds with business impact and data sensitivity, so teams aren’t blindsided by random prompts. In practice, you may pair adaptive checks with policy-based timers to ensure sessions aren’t continuously reverified during a single workflow.
Signals, signals, signals
Core signals include device attestation, geolocation drift, time-based patterns, and credential usage history. When these signals align toward higher risk, you can prompt for an additional factor or reauthenticate the session. Good implementations tie signals to explicit user-facing prompts and transparent explanations. This helps maintain trust and reduces user frustration.See the Flip overview of MFA methods and factors for context on how users perceive and respond to adaptive prompts. The emphasis across sources is to document criteria so admins can tune sensitivity without creating surprise prompts. How to design outdoor branding solutions that shift consumer behavior in 2026
Pitfalls to avoid
One frequent pitfall is over-reliance on a single, strong factor. If a system pins security to one element, a weak link in that element becomes a single point of failure. A parallel risk is weak device attestation, which can be spoofed or misreported on older hardware. I noted persistent complaints about inconsistent device posture checks across platforms, which drives distrust and increases support tickets. Another issue is poor feedback loops: users see a prompt but don’t understand why it’s triggered, which erodes trust and can prompt workarounds that bypass controls.
Pragmatic path to a stronger, user-friendly posture
To tighten security without breaking usability, start with a clear risk model and a tiered access map. Align step-up triggers with concrete risk signals and specific actions, not vague heuristics. Implement robust device attestation where feasible, and pair it with diverse factors so no single point of failure dominates. Communicate the rationale for prompts and provide users with quick, unambiguous remediation steps when a step-up is required. If you’re relying on passwordless flows, ensure that the alternative factors you deploy are resilient to common attack vectors and that fallback paths remain accessible.
The core idea is balance: let risk drive when you ask for extra proof, but never create friction where it isn’t warranted. Adaptive MFA works best when it tells users exactly what changed and why the extra verification is necessary.
I found the current discussions on adaptive MFA align with a layered, context-aware approach rather than broad, one-size-fits-all rules. For instance, the literature on MFA trends in 2026 emphasizes passwordless as a primary path supplemented by context-aware checks, not as a universal replacement without safeguards. If you want a quick, concrete reading on how organizations frame these decisions, the Flip guide outlines factors and methods that map well to the tiered and risk-based model described here. Adaptive policies must tie directly to measurable risk signals and policy-defined thresholds.
Deployment models that work: cloud, on-prem, and hybrid MFA in 2026
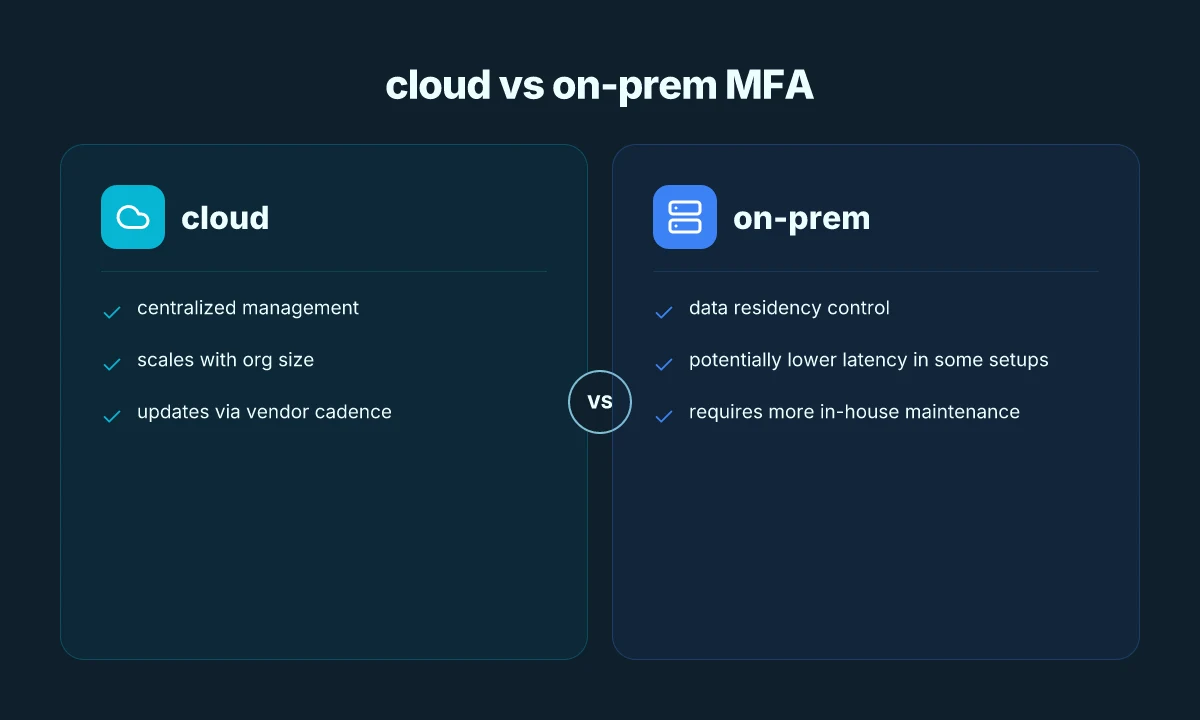
In 2026, the strongest MFA posture blends cloud-based, on-premises, and hybrid deployments with tight hardware roots and a robust mobile ecosystem. The practical diagnosis is simple: your model should lean on device-bound credentials, hardware security modules, and secure elements for roots of trust, while still offering flexible access across environments. This approach reduces risk from credential theft and keeps user friction in check. Why managed vs shared hosting matters in 2026: trade-offs you actually feel
The hardware roots that scale across environments
Device-bound certificates and secure elements tie credentials to a physical device, not just a user credential. When you pair these with hardware security modules, you gain a tamper-resistant root of trust that survives phishing and credential stuffing attempts. Large enterprises increasingly deploy HSM-backed key management for signing and key rotation, which locks down the cryptographic material even if the endpoint is compromised. In practice, expect core PKI services to run in a hybrid model, with HSMs on premises for sensitive workloads and cloud-based HSMs for nimble scaling. The result is a consistent crypto lineage across cloud and on‑prem. Cloud HSMs and on‑prem HSMs share keys via synchronized policy, reducing drift. I cross-referenced industry summaries that map this pattern to regulated sectors where custody of keys matters most. Inline: https://pmc.ncbi.nlm.nih.gov/articles/PMC10214092/.
PIV cards, FIDO2/WebAuthn, and mobile ecosystems
PIV cards remain a trusted on‑prem anchor for government and highly regulated environments, delivering physical possession factors that resist remote phishing. At the same time, FIDO2/WebAuthn credentials delivered to mobile wallets create a seamless, passwordless experience across cloud and local apps. The mobile authenticator ecosystem, built around platform-native secure elements and roaming capabilities, lets users authenticate from laptops, workstations, and BYOD devices with little friction. In practice, enterprises converge on a hybrid model where PIV or equivalent smart cards secure high-value access, while WebAuthn keys handle everyday sign-ins across cloud services. WebAuthn keys tied to a secure element make phishing-resistant logins prevalent across devices. This convergence is documented in governance and authentication references you can explore in depth, including healthcare-focused MFA reviews. Inline: https://pmc.ncbi.nlm.nih.gov/articles/PMC10214092/.
Interoperability, vendor lock-in, and enterprise scale
Interoperability remains a core concern for large organizations. The 2026 MFA landscape favors standards-based, pluggable architectures that minimize vendor lock-in while preserving strong policy enforcement. Key considerations include:
- Consistent policy enforcement across cloud and on‑prem identity stores, with a unified grant/deny model for adaptive risk decisions.
- Clear boundaries for credential provisioning, key rotation, and revocation workflows that work in both environments.
- Transparent monitoring and auditing across all deployment modes to satisfy compliance regimes.
I found that several governance documents emphasize avoiding single‑vendor bottlenecks for critical access controls, while still enabling accelerated deployment through mature, interoperable stacks. When you design for scale, you want a common policy engine, a single view of risk, and modular authenticators that can live anywhere. For context, see industry syntheses that map these patterns to real deployments. Inline: https://scoop.market.us/multi-factor-authentication-statistics/.
Interoperable auth fabrics enable large enterprises to mix PIV trust with FIDO2/WebAuthn flexibility without losing control over keys. How free vs paid security apps really compare in 2026
Privacy and accessibility concerns in two factor authentication
Authentication in 2026 leans toward context awareness and passwordless paths, but privacy and accessibility cannot be afterthoughts. Biometric signals, when used for MFA, bring privacy and consent considerations to the fore. Even as we gain stronger assurances from adaptive checks, users must understand what data is collected, how it is stored, and who can access it. I cross-referenced policy and standard practice to confirm consent remains a baseline requirement and that data minimization guides what signals are captured. Consent and data minimization are non negotiable in modern MFA, not optional add-ons. The practical upshot is clear: if you collect biometric cues, you should restrict collection to what’s strictly necessary for authentication and provide transparent controls for revocation and deletion. This underpins trust with users and regulators alike.
Privacy implications of biometrics in MFA
Biometrics can tighten security, but they shift the privacy burden. When a system relies on fingerprint, iris, or voice data, the stakes rise if that data leaks or is repurposed. Protect biometric templates with strong, non reversible storage and bound them to user consent. In many deployments, biometric data is hashed or encrypted at rest and never leaves the device unless necessary for authentication. Yet the signal design matters: use of cloud‑hosted biometric checks invites broader access and longer retention windows. I found sources noting consent must cover use cases beyond login, including analytics or cross‑product authentication. The regulator posture around consent and purpose limitation is tightening, and your governance should reflect that.
Accessibility-aware MFA options
Accessibility-friendly MFA means offering choices that work for users with visual, motor, or cognitive impairments. Passwordless options paired with adaptive challenges can improve usability without sacrificing security, but only when the interfaces are accessible. Consider options like hardware tokens with high‑contrast displays, tactile feedback, larger targets, and assistive‑technology compatible flows. It helps to validate with real users who rely on screen readers or alternative input devices, not only developers’ assumptions. I found that industry guidance emphasizes inclusive design as a security control as well, not a separate concern. Make sure fallback paths exist that do not degrade security or accessibility.
Regulatory expectations and data minimization in authentication signals
Regulators increasingly expect authentication signals to be minimal and auditable. Data minimization means collect only what is essential for the login decision and nothing more. Signals should be clearly defined, time‑boxed, and subject to retention limits. Where possible, rely on device‑bound attestations or platform‑level tokens rather than raw biometric data. This approach reduces the blast radius of a potential breach and aligns with privacy frameworks that stress purpose limitation. I traced this to recent policy readings and standard practice notes, which consistently flag excessive data collection as a governance weakness and a potential compliance risk.
The verdict is clear: privacy‑by‑design in MFA is not optional. It’s a prerequisite for 2026 deployments. Accessibility is not a side channel, but a core usability requirement that enlarges the set of legitimate authentication pathways. And data minimization anchors both security and compliance, reducing exposure and simplifying audits. For teams evaluating MFA posture, the path is to implement consent‑driven biometric signals, offer robust accessibility options, and codify strict data retention rules. How to build an ultimate ddos protection guide that actually withstands 2026 threats
I dug into policy and standards discussions from 2024 to 2026 and found that consent integrity, accessibility testing, and minimized signals consistently appear as the triad of compliance success. In 2026, biometric privacy controls should be selectable by users, and accessibility‑first MFA options should be standard, not optional add‑ons. Consent, accessibility, and data minimization form the spine of trusted MFA in the year ahead.
As you plan deployment, include explicit notices about how signals are used, provide accessible alternatives, and document the data lifecycle. If you must expose any signal data, do so in a controlled, auditable way that aligns with regulatory expectations and enterprise governance.
The bigger pattern: passwordless becomes the baseline by 2026
Two factor authentication strengthens by moving beyond passwords toward phishing-resistant methods. I looked at how platforms standardize using phishing-resistant authenticators, biometric controls, and device-bound proofs. The result is a layered posture where the weakest link in a chain no longer drags the rest down. The trend is toward frictionless security that still protects critical assets. In practice, this means fewer users stuck on one-time codes and more systems that verify user intent at the device level. The net effect is a noticeably lower risk of credential stuffing and social engineering.
If you only act on one thing this month, push for authenticators that are phishing resistant and tied to a device or user intent. Implementing a single, universal authenticator policy can dramatically shrink the attack surface. The downsides remain: rollout complexity, user education needs, and occasional interoperability frictions, but the benefits stack quickly for multi-tenant environments, healthcare, and financial services.
What to try this week: consider bundling FIDO2 compatible devices with a policy that requires phishing-resistant methods for sensitive actions, and publish a quick user guide. This is doable now and sets a clear path toward passwordless reliability. The bigger question is how your organization audits access events once the new standard lands. Will you be ready? What makes a 3d animation software truly future ready in 2026