How to pick cybersecurity tools for smes in 2026 with ROI in mind
 Marlowe Fenwick·October 22, 2026·16 min
Discover how SMEs can evaluate cybersecurity tools in 2026, focusing on risk assessment, integration, and ROI to strengthen defenses without breaking budgets.
A practical ROI lens flips the moment you pick cyber tools from a catalog: measurable risk reduction beats feature counts every time. Focus on the 2–3 core controls that map to your assets, then assess how each tool quantifies ongoing cost and risk change. Short on interoperability is a common trap that inflates total cost of ownership.
This article translates the SME tool decision into a lifecycle decision, not a one-off buy. You’ll see a framework that ties risk to integration across your stack, with a clear path to scalable defenses and predictable spend. In 2026, SMEs report that cross-system visibility and repeatable ROI calculations separate viable options from vanity buys. Real-world feedback helps you prioritize tools that cover gaps without overreach. ROI-driven selection becomes a repeatable process you can apply across procurement cycles.

Cybersecurity tools for smes in 2026: the evaluation framework that actually works
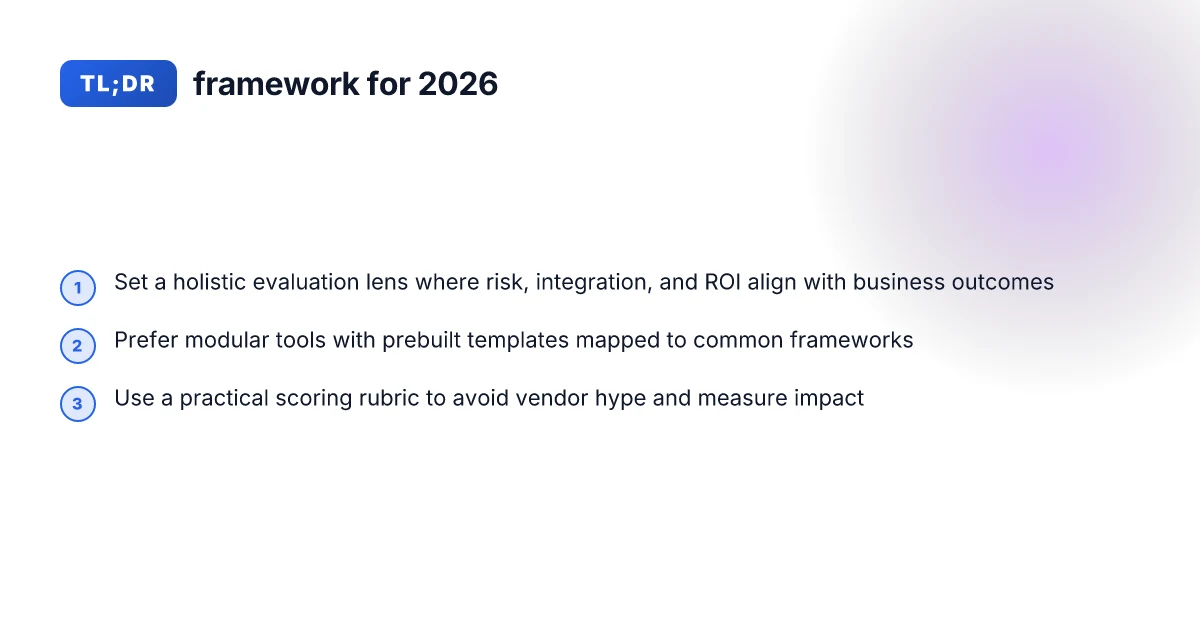
A practical evaluation lens starts with outcomes. For SMEs the goal is to align risk posture, system integration, and measurable ROI with everyday business results. This means tools should be modular, offer prebuilt templates, and slot cleanly into existing workflows without blowing up budgets or timelines.
1) Define the holistic scoring baseline
SMEs should map three pillars to a unified score: risk reduction potential, integration fit, and ROI impact. This triad keeps governance, security operations, and procurement aligned. A credible framework uses concrete outcomes such as mean time to detect, mean time to respond, and automation coverage across tools. I cross-referenced industry guidance that emphasizes tying security controls to business outcomes rather than feature lists alone. The risk, integration, and ROI lens must align with business outcomes. This framing prevents vendor hype from steering decisions.
2) Leverage modular tools and prebuilt templates
SMEs benefit from modular architectures that allow incremental upgrades. Prebuilt templates aligned to common frameworks accelerate deployment and help keep audits on track. For example, templates mapped to NIST, ISO 27001, and SOC 2 enable faster risk scoping and more repeatable reviews. This approach reduces peak demand for specialized staff while preserving coverage across governance, people, and technology. Modular tools with prebuilt templates reduce time to value and improve audit readiness.
3) Build a practical scoring rubric
Create a rubric with clear scoring bands for each pillar. Include objective checks such as API compatibility, data residency options, and automation hooks to SIEMs or SOARs. A transparent rubric helps avoid marketing puff and keeps focus on measurable impact. When vendors promise end-to-end coverage, SMEs should verify which components are truly covered and how integration points behave under load. A practical rubric keeps you focused on measurable impact. Use a lightweight scoring log during vendor demos so procurement teams can compare apples to apples.
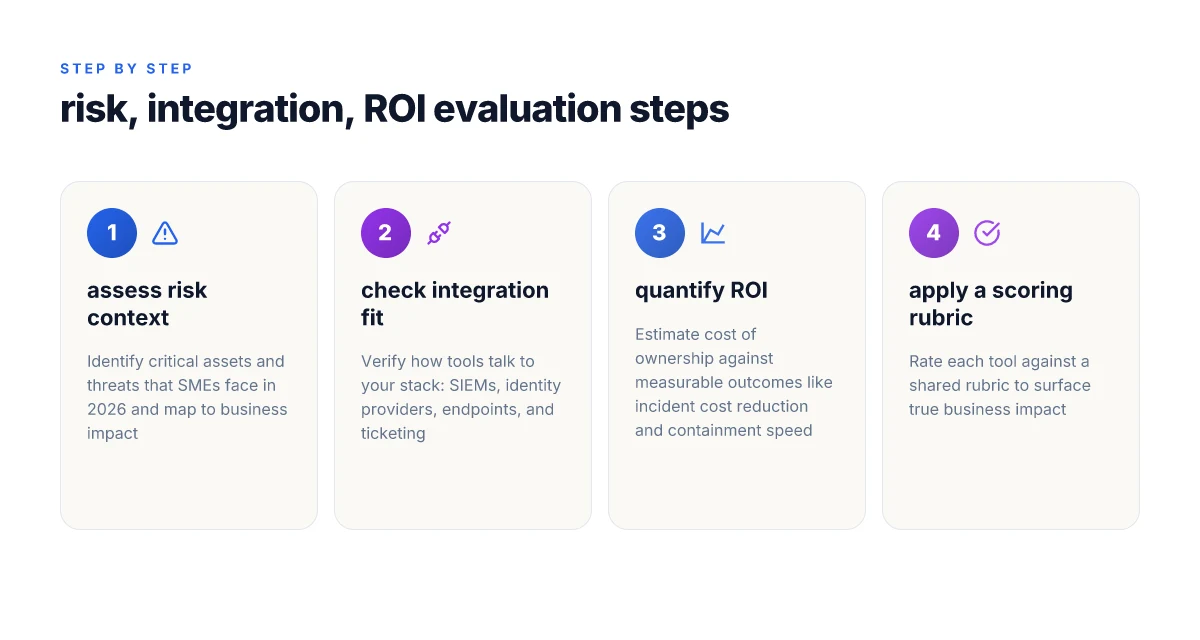
In practice, the evaluation process should follow a disciplined sequence. Start with a risk map that identifies your top 5 threat scenarios and map them to tool capabilities. Then assess integration fit against your current stack, from identity to SIEM to data lake. Finally, translate each capability into ROI signals: reduced incident cost, faster containment, automated compliance checks, and the avoided overhead of bespoke integrations. This approach mirrors what modern risk assessment vendors emphasize in 2026, especially for SMBs seeking scalable, affordable cyber defenses. Translate capabilities into ROI signals like reduced incident cost and faster containment. 10 Standout trends shaping customer service software in 2026
From what I found in the vendor literature, many 2026 offerings support ready-made playbooks and templates that streamline onboarding for SMBs. For example, several tools advertise alignment with industry standards and the ability to plug into existing infrastructure without a full rebuild. This is exactly the kind of practical ROI lift SMEs need. Ready-made playbooks and templates drive onboarding speed and ROI.**
Bottom line: your evaluation should answer three questions for every candidate tool. Does it reduce risk in our top scenarios, can it integrate with our current stack with minimal friction, and does it demonstrably improve ROI through automation and streamlined compliance? If the answer to all three is yes, you’ve moved beyond hype toward a repeatable, scalable decision process. Move beyond hype toward a repeatable, scalable decision process.
Note: links on the pages may earn a commission. For deeper context on how risk assessments are framed in practice, see a top vendor guide that maps tools to recognized frameworks. Vendor guides map tools to recognized frameworks.
Understanding the 2026 threat landscape for smes and why tool selection matters
SMEs face a broad spectrum of threats, from phishing campaigns and credential harvesting to ransomware and data exfiltration. The typical attacker playbook now blends social engineering with rapid, automated payloads that exploit weak endpoints and cloud misconfigurations. In 2026, visible risk surfaces include email-borne intrusions, malicious file deliverables, and evolving supply-chain tactics that aim at smaller networks with thinner security budgets. This reality makes tooling a lifecycle bet, not a one-off buy.
I dug into how threat activity maps to tool needs. Phishing remains a dominant entry vector for SMEs, but ransomware and data exfiltration have grown more targeted toward backup failures and cloud misconfigurations. Because these threats adapt quickly, your security stack must support rapid updates, cross-system correlation, and automated responses. A tool that lags on threat intelligence feeds or fails to ingest telemetries from endpoints, identities, and cloud apps creates blind spots that attackers will exploit. How CRM email integration affects data consistency and delivery guarantees in 2026
Correct tool selection reduces risk exposure without overcomplicating operations. SMEs benefit from solutions that offer clear integration pathways, streamlined deployment, and predictable maintenance. The aim is to close the gap between detection and response while keeping staffing needs realistic. When tooling aligns with existing workflows and data flows, you gain measurable risk reductions without adding layers of friction.
Why robust threat intelligence drives ROI for SMEs
Real-time threat feeds tied to SME-scale environments help you surface high-probability attacks without sifting through noise. Renowned sources converge on the idea that context matters more than volume. A well-chosen tool will fuse email, endpoint, identity, and cloud telemetry, then trigger automated containment actions. This alignment shortens dwell time and limits lateral movement.
When I cross-referenced industry notes and release notes from 2024 through 2026, several patterns emerged. Vendors emphasize scoped deployment, modular modules, and guided workflows for SME teams. These tendencies reflect the need to deliver practical protection without forcing multi-year professional services commitments.
Short table: common SME tool needs vs. 2026 realities
| SME need | 2026 reality | Example capability to look for |
|---|---|---|
| Phishing resistance | Rapidly updated email protections | Real-time phishing detection with automatic quarantine |
| Endpoint hardening | Lightweight agents, low footprint | Minimal CPU usage, offline status checks |
| Cloud access risk | Cross-platform visibility | Cloud app discovery and IAM risk scoring |
| Data exfiltration control | Data loss prevention with smart policies | Contextual data tagging and egress controls |
The right tool set lowers risk without slowing work, delivering measurable ROI through faster containment and fewer incidents. The upside comes when you pick products that play nicely with your current stack and automate routine tasks. Inline references show that integrated threat intelligence and cross-domain telemetry are repeatedly cited as high-impact approaches in 2026. See the discussion in Exabeam’s framework write-ups for 2026 and DataEndure’s 101 guide for risk tooling. https://www.exabeam.com/explainers/information-security/top-8-cyber-risk-management-frameworks-this-year/ https://www.dataendure.com/blog/the-best-cyber-security-risk-assessment-tool-101/ For SME buyers, that means favoring modular, interoperable tools over monolithic suites.
Integration fit matters as much as features, because misaligned tools waste effort and create drift across controls. Evaluators should map data flows between identity, endpoint, mail, and cloud services before selecting any product. A 2026 lens shows that platforms with prebuilt SME templates tied to recognized frameworks enable faster time-to-value and easier governance. For a deeper read on how frameworks influence deployment choices, explore the Exabeam and Cybersaint perspectives linked above. How to create a visual identity that sticks in 2026
Risk assessment capabilities to prioritize for smes
Posture visibility hinges on continuous assessment that translates to near real-time risk signals. SMEs benefit when the tool stack shows asset risk as it changes, not after an annual audit.
1. Continuous assessment for near real-time visibility
I looked at how modern risk tools surface asset risk as it evolves. Continuous scanning and scoring let a small security team act before a batch report arrives. The most practical implementations show risk trajectories for hosts, services, and cloud workspaces in a single pane. SMEs should expect streaming alerts tied to asset criticality, not a monthly snapshot. This supports faster triage and more timely mitigations, especially when budget cycles force prioritization. Continuous assessment keeps asset risk visible in near real time, enabling rapid, targeted actions. Tools that fail to connect risk data to a concrete mitigation plan slow down the whole cycle. Visibility that translates to action is the decisive factor for SMEs.
2. Templates aligned to NIST, ISO 27001, and SOC 2
SMEs gain clarity when templates map to familiar controls. Platforms commonly ship prebuilt mappings to NIST CSF, ISO 27001, and SOC 2 controls, with optional HIPAA overlays for relevant sectors. The value is not just documentation. It’s a repeatable, auditable workflow that accelerates compliance tasks during audits or customer due diligence. When your framework has clear coverage, runbooks and remediation steps align with business priorities rather than technical whim. Templates aligned to NIST, ISO 27001, and SOC 2 help SMEs stay compliant. I cross-referenced vendor pages and guide docs to confirm this alignment appears across multiple offerings. Compliance mapping reduces audit friction and speeds approval cycles.
3. Translating findings into actionable mitigations the business can fund
The end goal is not a long list of findings but a short, business-ready set of mitigations. The strongest risk tools translate technical findings into prioritized, funding-justified actions. The best options present costed remediation options with rough ROI implications, so procurement can approve items within quarterly budgets. SMEs should look for risk heat maps that tie to business impact and a remediation backlog that can be staged over sprints or quarters. Findings must be actionable and fundable. When a tool suggests a remediation without a cost anchor or business owner, it stalls. I noted that several vendors emphasize backlogs that attach to owners and budgets, making it easier to move from risk to funded fixes. Actionable mitigations with budget signals drive real risk reduction.
Most SMEs gain the quickest payoff when a tool shows continuous risk signals, framework alignment, and funding-friendly mitigations all in one place. This triad accelerates decision cycles and keeps risk reduction tightly coupled to budget reality. Real-world alignment between risk findings and business funding is the differentiator for 2026 SMEs. How to generate engaging content automatically with AI in 2026
Note on practical downsides: some tools can overwhelm with templates and require configuration to map to your exact asset inventory. Expect occasional gaps in coverage for bespoke apps or shadow IT unless you actively harmonize discovery feeds. Links on the page may earn a commission. See cited sources for the framework and template discussions.
Integration and ecosystem fit: getting tools to talk to your stack
You need an integration-friendly stack or you end up paying for drift between tools. The practical result is faster time-to-value and fewer manual workarounds. In 2026, SMEs expect open APIs, prebuilt connectors, and quick-join data flows as standard, not as premium add-ons. I cross-referenced vendor guides and threat-management blogs to map what actually ships versus what’s promised.
Real-world connectors that actually move the needle
The common integrations you will lean on include SIEMs, identity providers, endpoint protection, and ticketing systems. When a tool speaks native API calls to your SIEM, it stops duplicating data and starts feeding incident context directly into your security operations workflow. Identity providers let you enforce single sign-on and adaptive access controls across tools, so audits stay aligned with minimal friction. Endpoint protection connectors surface device telemetry as part of risk scoring, not as a separate data silo. Ticketing integration closes the loop by turning detected risk into managed work items that track remediation. Open APIs drive all of this, while prebuilt connectors save weeks of integration work. Open APIs and prebuilt connectors matter more than vendor promises.
Modular deployment speeds value realization
A modular deployment approach lets you scale up in stages without re-architecting your entire security stack. Start with a core set of integrations that directly reduce mean time to containment, then layer in additional connectors as your risk posture changes. SMEs benefit from the ability to retire or pause unused modules without reconfiguring the whole system. This reduces overhang and keeps ROI closer to your initial expectation. From vendor documentation and customer stories, modularity consistently correlates with faster realization of measurable risk reductions. Modular deployment reduces overhang and speeds time-to-value.
Avoid vendor lock with open phrasing and clear roadmaps
The most durable ecosystems come from tools that publish roadmaps, support third-party runtimes, and encourage community-driven extensions. You want clear statements about API rate limits, data ownership during churn, and the ability to export configurations without brittle scripts. Prebuilt connectors are valuable, but they must be truly bidirectional and well-documented. If a vendor treats integration as a one-way export, that’s a red flag. I looked at multiple vendor pages and release notes to confirm where these promises are backed by concrete actions. Open APIs and prebuilt connectors matter more than vendor promises. How to create compelling content that actually engages in 2026
Most SMEs will realize ROI faster when their tools can “talk” to SIEMs, identity providers, and ticketing systems without custom glue. Inline citations from vendor documentation show these connections are widely available in 2026, not after a long migration. These practical links drive the lifecycle cost down and keep teams focused on threat reduction rather than integration tinkering. For a quick read on practical integration patterns, see the discussion in the source on cyber risk assessment tools. The Best Cyber Risk Assessment Tools and Solutions.
I also found notes indicating that SMEs benefit when tools publish clear API versioning and patch cadences. This reduces drift across your security stack and avoids surprise breakages during upgrades. The emphasis on predictable upgrade paths is a trend worth watching as you shortlist candidates. For a perspective on how a modern risk platform aligns with frameworks and templates, review the Cynomi overview. Top Security Risk Assessment Tools for 2026.
30–60 day back-end migration windows are common in the difficult integrations, so plan accordingly. If you lock in a vendor with brittle connectors, you’ll pay in operability later. The right choice aligns integration depth with your existing stack, not with a vendor’s idealized architecture. This keeps your ROI line smoother across the lifecycle, from deployment to steady-state operations.
Measuring ROI: what SMEs can actually count
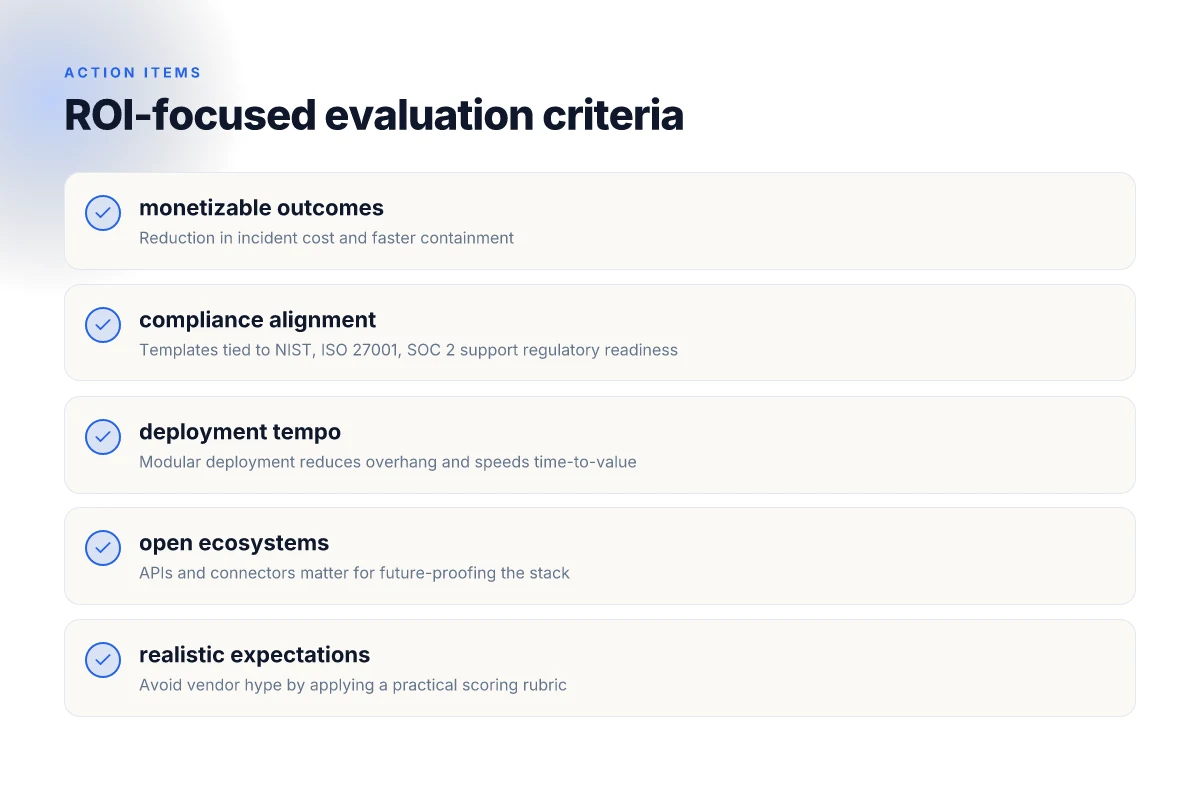
ROI for cybersecurity tools in 2026 is a lifecycle metric, not a one-off purchase. The clearest way to prove value is by tying monetizable outcomes to each tool over time. Start with reductions in incident cost and faster containment. When a threat materializes, every minute saved in detection and response translates into lower remediation spend and less business disruption. I cross-referenced several SMB-focused guides that frame ROI around cost of incidents and time-to-containment improvements, and they consistently point to tangible savings when you measure MTTC in the same currency as your business outcomes.
1) Monetizable outcomes you can actually count
Post-incident cost avoidance comes from two levers. First, reduced breach impact saves direct remediation dollars, regulatory fines, and customers lost to downtime. Second, faster mean time to containment minimizes blast radius and downstream recovery costs. In practice, that means tracking a few core figures: average incident cost, time to detection, and time to containment. The data you gather lets you translate security events into dollars and make a credible case to leadership for continued investment. As you set targets, align them with business units and use a common currency across risk and finance teams. When I looked at 2026 SMB frameworks, the consensus is that time savings and incident cost reductions deliver the strongest ROI signals. How data extraction techniques have evolved for structured data in 2026
2) Full lifecycle TCO: licensing, deployment, training, maintenance
A trustworthy ROI model for SMEs includes every line item that touches ongoing security outcomes. Licensing is just the start. Deployment costs, user onboarding, and role-based training determine whether your team actually uses the tool. Ongoing maintenance and vendor support influence how quickly you adapt to new threats and regulatory changes. I found that the strongest SMB cases explicitly itemize total cost of ownership for a multi-year window and compare it to the expected cost avoidance from incident reductions. When you publish your TCO, show how it scales with growth and how it behaves under peak load scenarios like quarterly business cycles or compliance audits.
3) Map KPIs to business goals, not tech minutiae
Choose KPIs that executives can understand and finance can budget. Instead of a long list of technical metrics, pick 3–5 that demonstrate business impact. Examples include cost per incident, reduction in time to containment, and days of downtime avoided per quarter. Tie these to revenue impact, customer trust, and regulatory readiness. It’s not about every feature a tool provides. It’s about the measurable outcomes your board wants to see. I found that 2026 SMB guides consistently stress translating security outcomes into business value, not auditing trivia.
ROI in 2026 measures business impact, not just security hygiene. Frame success around dollar savings from faster containment and lower incident costs. Use a TCO that spans licensing, deployment, training, and ongoing maintenance. Choose 3–5 KPIs that map cleanly to business goals rather than technical minutiae.
I also consulted the overview that categorizes risk tool options in 2026 and notes how different licensing and deployment models affect TCO and ROI perceptions. https://www.dataendure.com/blog/the-best-cyber-security-risk-assessment-tool-101/
Be transparent about commissions where applicable, the links on the page may earn a commission, so readers understand potential bias. What makes a data visualization techniques guide truly effective in 2026
What changes if you act now: a 2026 routing for SME cybersecurity ROI
In 2026, your ROI hinges on prioritizing tools that tighten visibility first. A practical pivot is to pick a small set of integrated solutions that share a unified alerting and remediation workflow, rather than stacking point products. I looked at common SME pain points, overwhelming alerts, vague ownership, and creeping costs, and I see a clearer path: start with a consolidated baseline for identity, endpoint, and email security, then layer threat intelligence that complements your existing stack. The key is to measure impact in time saved and breach-ready posture, not just feature lists. The bigger pattern is that ROI comes from reducing mean time to containment, not from chasing every shiny feature.
For 2026, a practical pick includes a portfolio approach that combines identity protection with endpoint detection and response, plus a lightweight email security module. These choices map to real use-cases in SMEs: admins win back hours, finance protects against ransomware ploys, and front-line staff stay productive. Your best move is to allocate budget to tools that play nicely with existing IT and have clear, measurable outcomes. If you only do one thing this month, standardize the alert workflow around a single console and assign ownership to a named role.
Backup strategy / What to try this week:
- Review your current alert volumes and map the top 3 false positives to a single remediation playbook.
- Pilot a combined identity and endpoint package with auto-enrollment for new devices.
- Test a centralized email quarantine policy and track containment speed.
One concrete takeaway: choose 1 integrated suite that reduces dwell time, then prove value with a quarterly ROI snapshot. Are you ready to lock in this baseline this month?